


Introducing SafeDep Model Context Protocol (MCP) Server to Secure AI Generated Code
On this page
Why build this?
SafeDep vet now exposes a Model Context Protocol (MCP) Server to secure AI generated code and protect against slopsquatting attacks, vulnerable and malicious packages. This feature is available to all the users of SafeDep vet, enabling IDE native software composition analysis (SCA) for AI generated code. To use this feature:
- Configure MCP clients (eg. Cursor, Claude Code) to use SafeDep
vetMCP server - Instruct the MCP Clients to use the MCP server before installation of any package
- Once setup, it will automatically vet all packages before installation by the editor
Adoption of AI Code Generation and Agentic Software Engineering opens up new attack vectors such as slopsquatting. It is imperative to have appropriate guardrails against attacks exploiting LLM hallucinations and prompt injection attacks against agentic coding tools to deploy vulnerable and malicious packages.
How to use SafeDep MCP Server
You will need an MCP client such as Cursor, Claude Code etc. used for AI code generation. Add the following to the MCP client configuration to use SafeDep vet MCP Server. For Cursor, it will be ~/.cursor/mcp.json file but will be different for other MCP clients.
{ "mcpServers": { "vet-mcp": { "command": "docker", "args": ["run", "--rm", "-i", "ghcr.io/safedep/vet:latest", "server", "mcp"] } }}Create a prompt or a rule instructing your AI Code Editor to use the MCP Server to vet all packages before installation. For Cursor, create a rule file in your project directory at .cursor/rules/vet-mcp.mdc with the following content:
---description: vet Open Source Packages using vet MCP serveralwaysApply: true---
Always use vet-mcp to vet any open source library package suggested by AI generated code before installation.Follow the rules below to use vet-mcp:
- Try to find the latest version. If not found, it is likely a slopsquatting vulnerability- Always check for critical vulnerabilities and malwareUsage
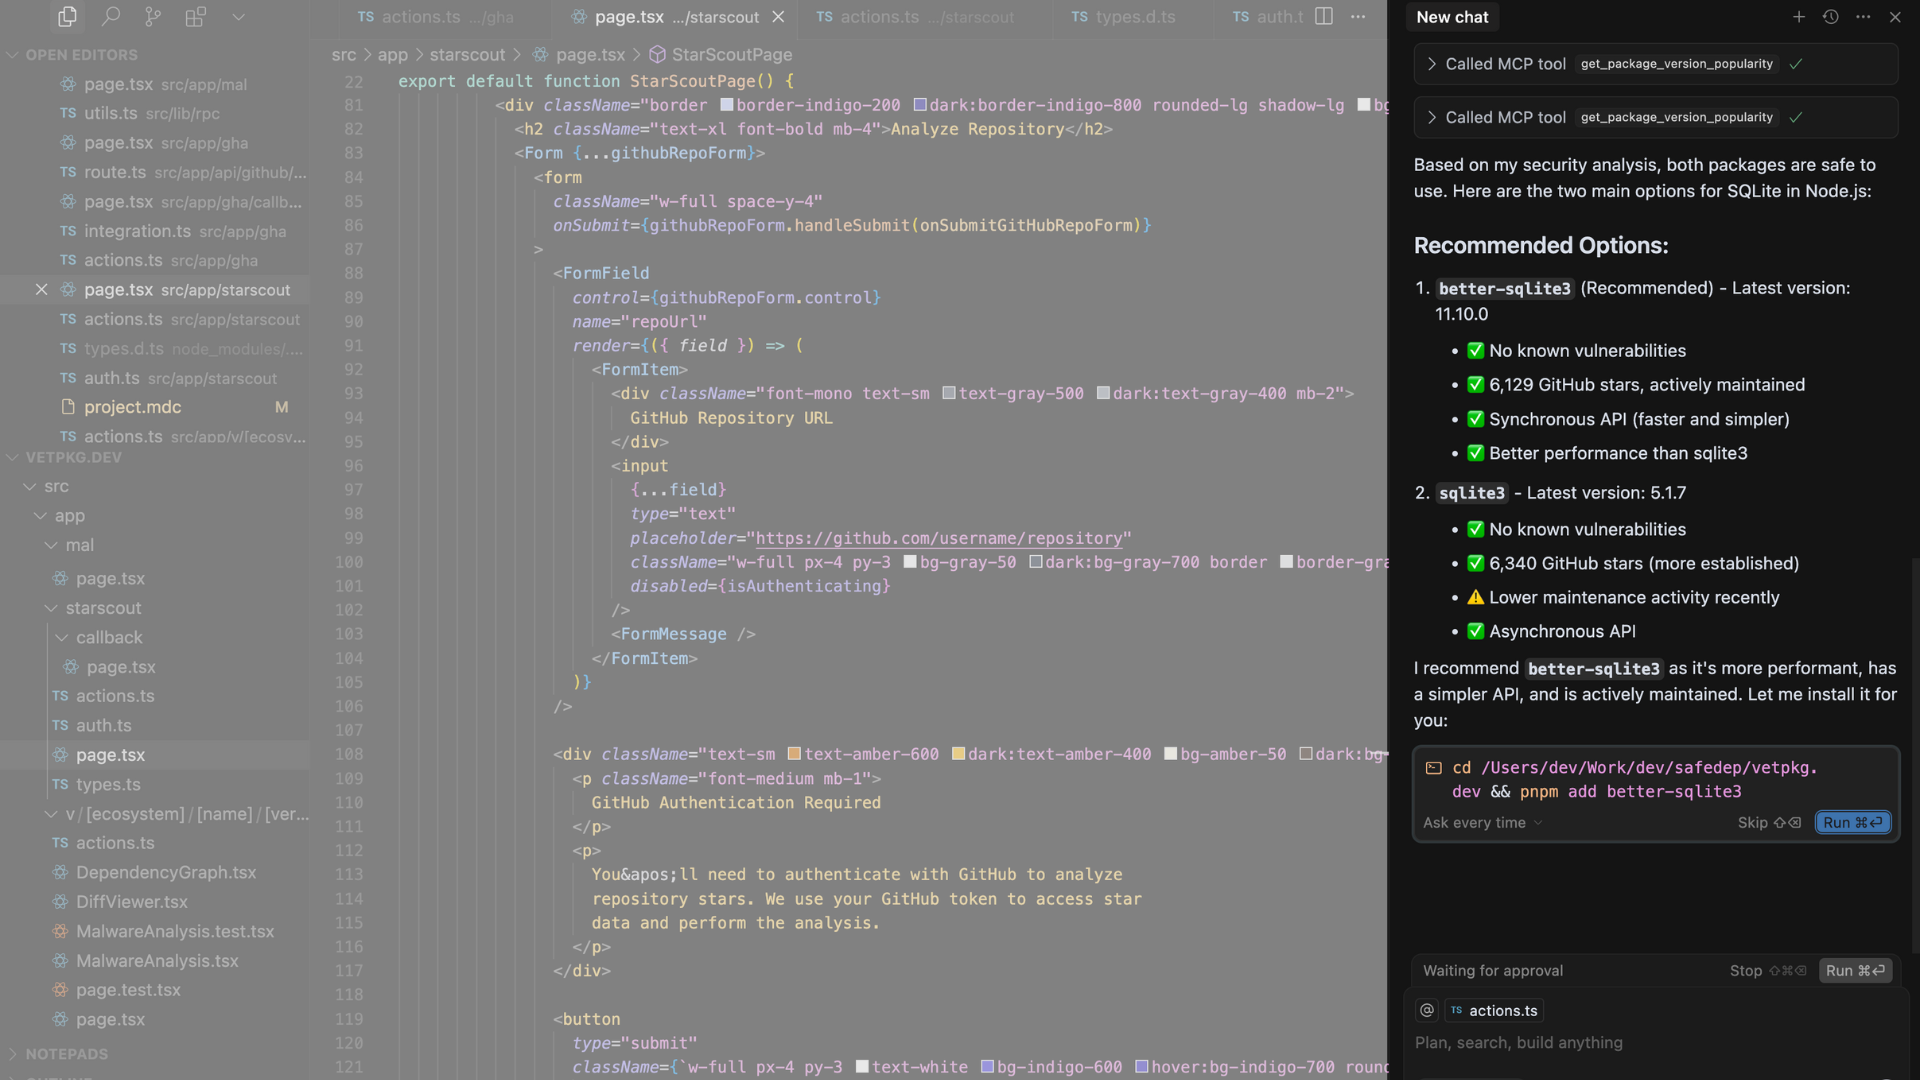
Once setup, it will automatically vet all packages before installation suggested by AI generated code.
AI Native Software Composition Analysis (SCA)
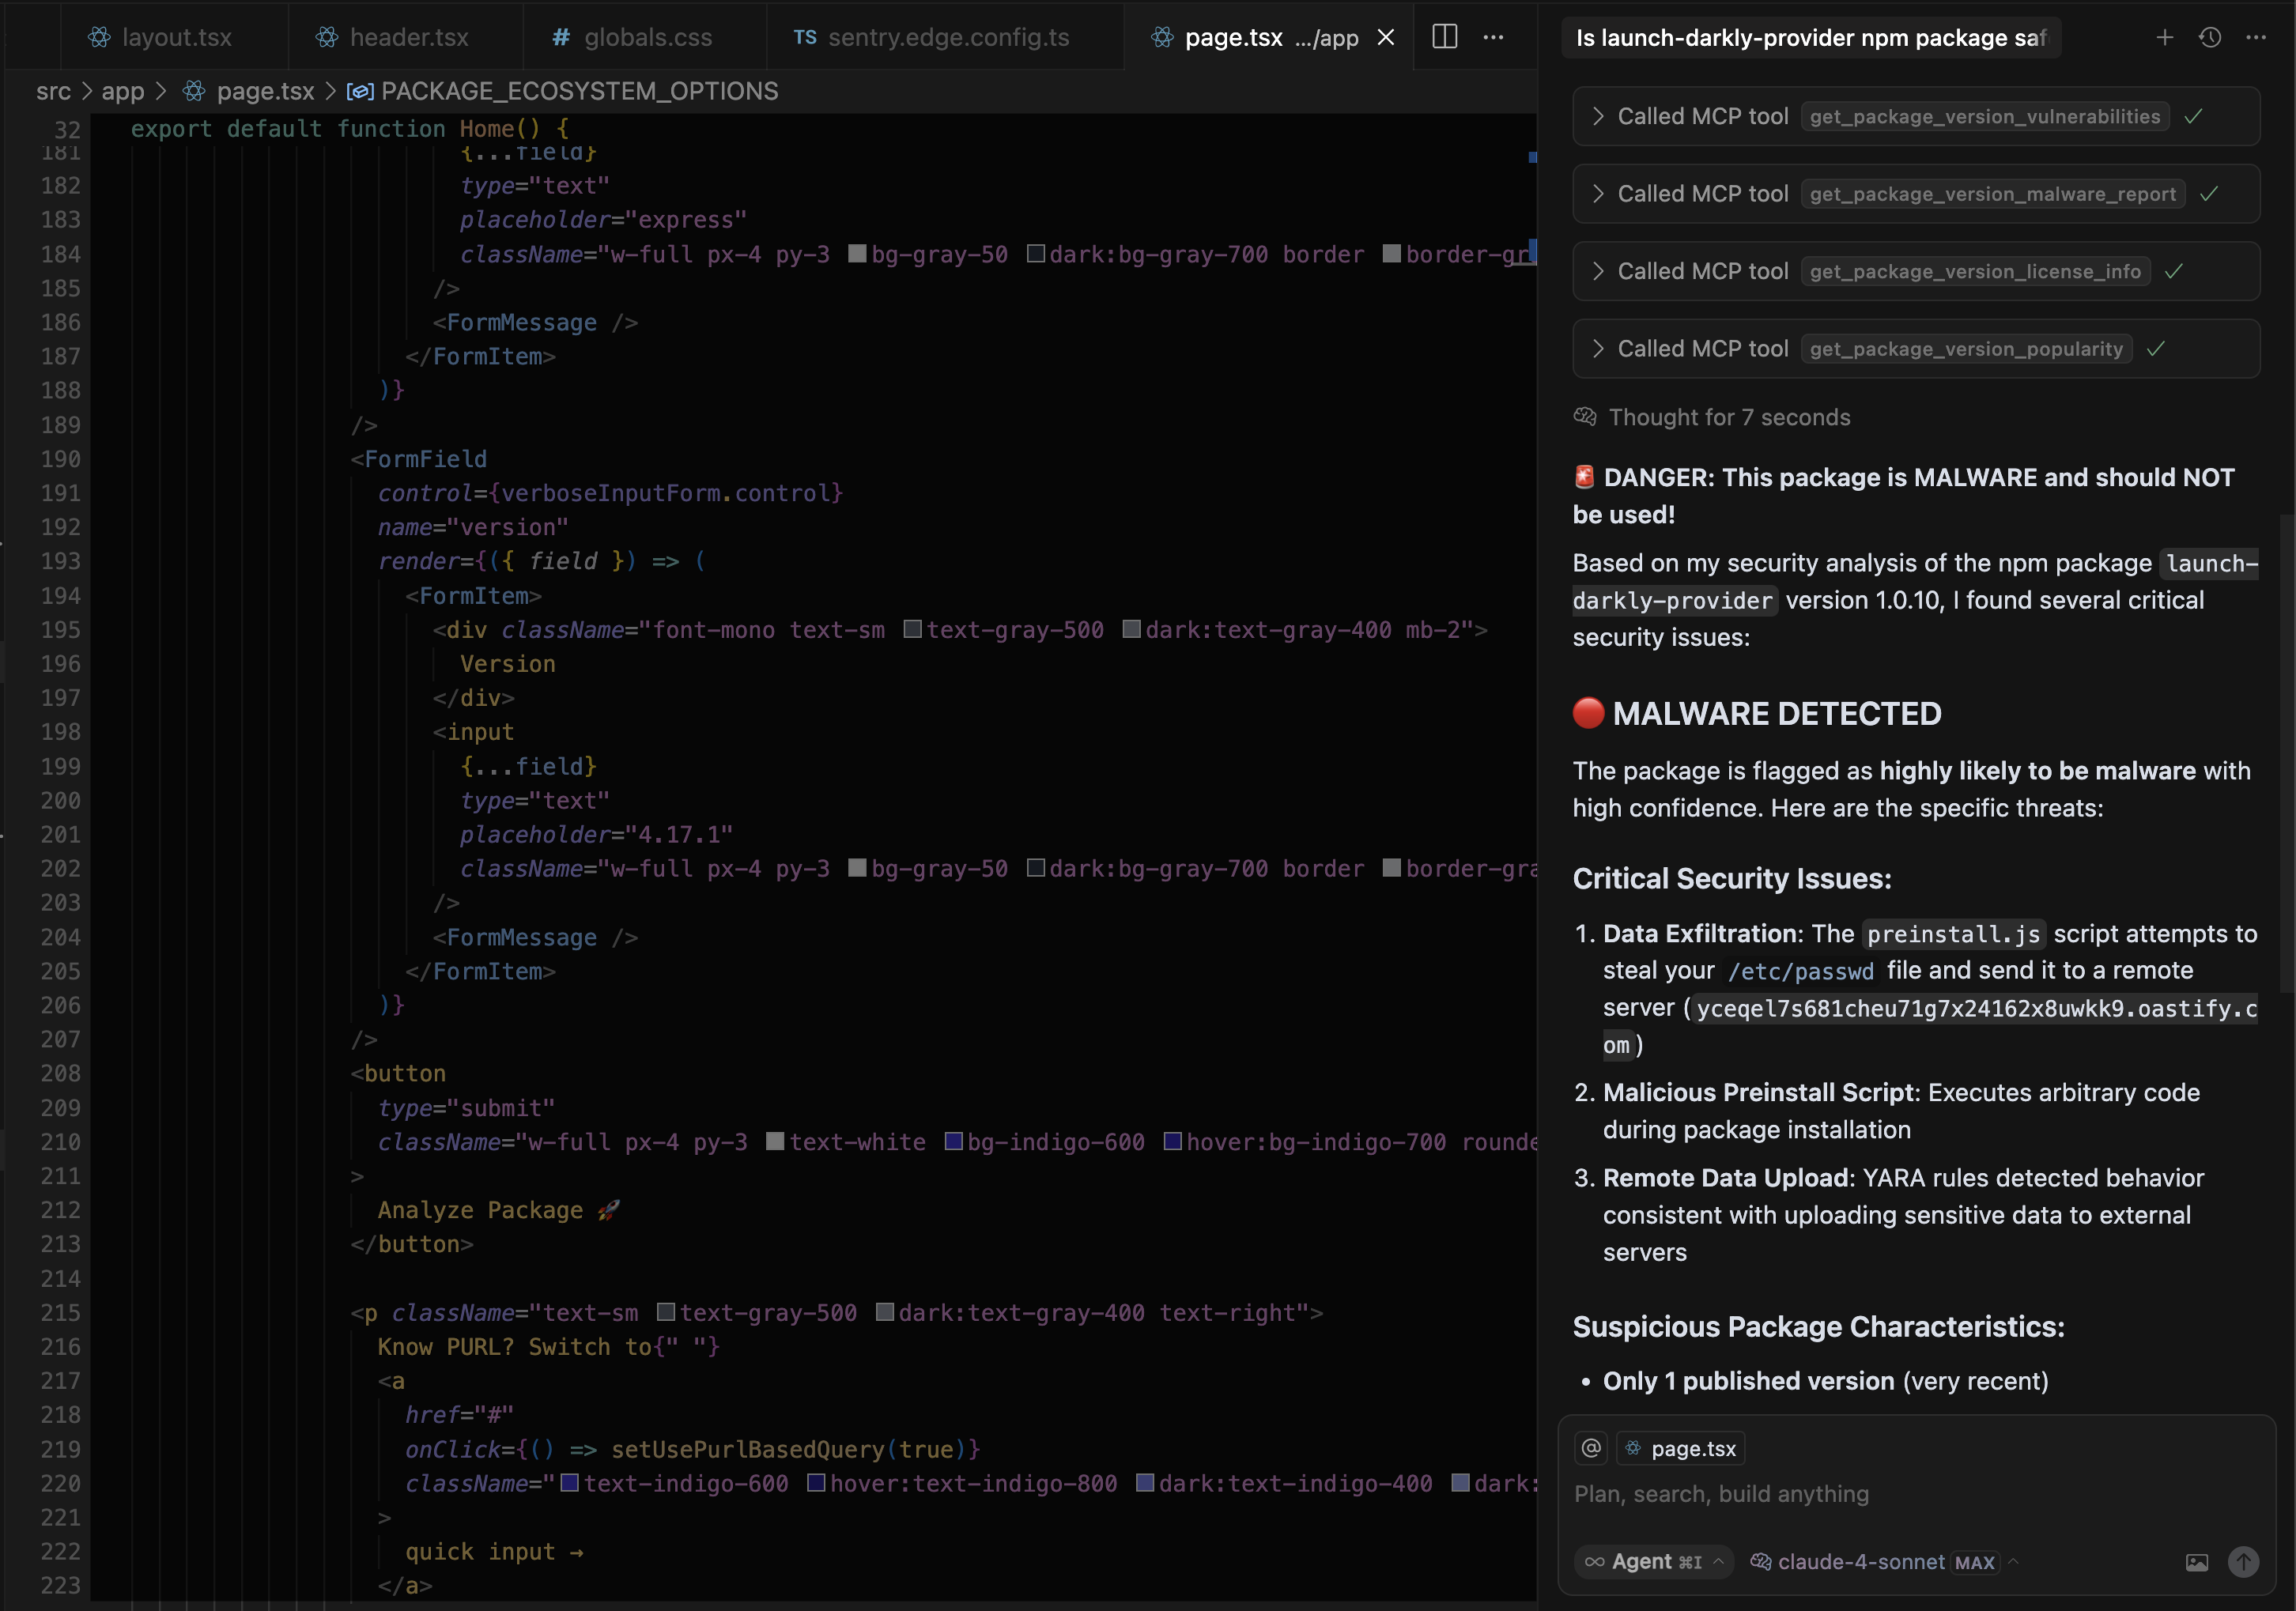
AI IDE chat interfaces can be used to ask questions about various packages and their vulnerabilities to make sure the code is secure.
For example, you can ask: Is npm package launch-darkly-provider safe to use before installation.
Note: launch-darkly-provider is a known malicious package that our systems discovered recently and is not safe to use. For near-real time protection against malicious packages, setup SafeDep vet in your CI/CD pipeline in addition to development environment.
How it works?
The MCP server is built using SafeDep vet as the foundational SCA engine. It is supported by SafeDep Cloud APIs to query for malicious packages that are being continuously updated using SafeDep Malicious Package Scanning service. For community contributions and support, open an issue on SafeDep GitHub or start a GitHub Discussion.
- mcp
- security
- ai-code-generation
- agentic-software-engineering
- slopsquatting
- prompt-injection
- sca
- supply-chain-security
Author

SafeDep Team
safedep.io
Share
The Latest from SafeDep blogs
Follow for the latest updates and insights on open source security & engineering
Introducing SafeDep Threat Intel
SafeDep Threat Intel gives SOC and cyber defense teams the malicious package intelligence behind SafeDep's platform, to query or to push into the tools they already run.
Mini Shai-Hulud Strikes Again: openapi-react-query-codegen
An attacker exploited a flawed GitHub Actions workflow to publish 10 malicious versions of @7nohe/openapi-react-query-codegen (671K downloads/month) via npm OIDC trusted publishing. The payload uses...
A malicious npm package hidden three dependencies deep: the ulid-xyz delivery chain
ulid-xyz is a remote access trojan we reported to OSV as MAL-2026-6672. It reached developers as a third-level transitive dependency of ioredis-xyz, a copy of the real Redis client planted in 28...
From YouTube Ad to Root: How a Fake TradingView Installer Delivers a macOS Stealer
A YouTube video ad impersonating TradingView delivered a fake .pkg installer. Inside: a self-healing LaunchAgent, an AES-encrypted V8 bytecode payload, and a Node.js MITM proxy trusted by a rogue...

Ship Code.
Not Malware.
Start free with open source tools on your machine. Scale to a unified platform for your organization.
