


Sneak Peak into SafeDep Cloud Development and SQL Queries
Software Bill of Material (SBOM) provides an inventory of all software components. However, they are useful only when a flexible query interface is built on top. In this post, we provide a #build-in-public preview of what we are building at SafeDep. We believe a flexible query interface on top of BOM solves important use-cases for OSS risk management and software supply chain security.
Register for SafeDep Cloud
Leverage the power of SafeDep cloud to build an organization wide SBOM, export as CycloneDX and execute flexible queries to discover actionable risks.
- vet
- sbom
- safedep-cloud
Author

SafeDep Team
safedep.io
Share
The Latest from SafeDep blogs
Follow for the latest updates and insights on open source security & engineering
eMudhra CA Key Compromise: Response Guide for Developers
Anyone can compute eight eMudhra intermediate CA private keys from public certificates. Browsers block the compromised intermediates, but CI runners, containers, JVMs and Go binaries can still trust...

Compromised LiteLLM 1.107.0 on PyPI Installs a Credential Stealer and Backdoor
Every wheel of LiteLLM 1.107.0 on PyPI installs a credential stealer and a remote code execution backdoor. Both run each time Python starts. The code is not in the upstream GitHub source.
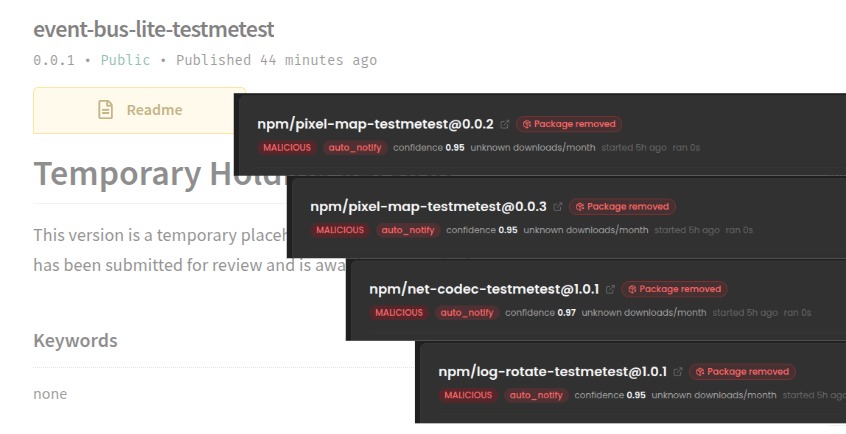
testmetest npm Packages Carry a Miasma-Family Worm
19 npm packages carry a Miasma-family worm that steals credentials, spreads to other packages and installs a wiper. The newest builds start the worm when an application loads the package.
Forged Commits Push a preinstall Dropper into hugo-paper and mevn-cli
An attacker pushed forged commits to the default branches of hugo-paper and mevn-cli. Running npm install or bun install in either repository downloads and runs a second-stage script from...

Ship Code.
Not Malware.
Start free with open source tools on your machine. Scale to a unified platform for your organization.
