


Introducing Container Image Scanning
On this page
Container images are a popular way to package and deploy applications. These are the deployable artifacts in modern cloud native world. However, they often contain vulnerabilities and malicious packages. Conventional container image scanning tools focus on vulnerability (CVE) identification for container images. However, malicious or compromised packages do not have CVEs. To protect against the risk of vulnerabilities and malicious packages, deployable container images must be evaluated for security risks. vet now supports scanning container images using --image flag.
Scanning Local Images
Container images available in local docker server catalog can be scanned using the following command:
vet scan --image redis:latestScanning Remote Images
vet will pull the image data if the container image is not available in local docker server catalog.
vet scan --image redis:latestScanning Local Tarballs
Exported container images can be scanned using the following command:
vet scan --image /path/to/image.tarThis tarball can be created using docker save command. This is useful when you want to scan a container image that is not available in local docker server catalog.
docker save redis:latest -o image.tarMalicious Package Scanning
Container scanning can be combined with malware detection using the --malware flag. It also supports various reporting formats including --report-cdx and --report-json for generating standardized output.
vet scan --image redis:latest --malwarevet scan --image redis:latest --report-cdx=report.cdx.jsonPolicy Driven Container Scanning
vet is designed as policy first. It uses a Common Expression Language based policy engine to allow flexible policies. For example, to prevent containers with malware or critical vulnerabilities from getting deployed, you can run vet with the following policy:
vet scan --image redis:latest --malware --filter 'vulns.critical.exists(p, true)' --filter-failNote: vet will always fail when a malicious package is detected.
Other scanning options
For more details on how to use vet with container scanning, please refer to the documentation.
Demo
Bugs and Feedback
Found a bug or have suggestions? We’d love to hear from you! Please open an issue in our vet GitHub repository. For discussions about vet and other SafeDep tools, join our friendly developer community on Discord. We’re always excited to connect with fellow developers and hear your thoughts!
- container-scanning
- malware
- security
Author
Kunal Singh
safedep.io
Share
The Latest from SafeDep blogs
Follow for the latest updates and insights on open source security & engineering
eMudhra CA Key Compromise: Response Guide for Developers
Anyone can compute eight eMudhra intermediate CA private keys from public certificates. Browsers block the compromised intermediates, but CI runners, containers, JVMs and Go binaries can still trust...

Compromised LiteLLM 1.107.0 on PyPI Installs a Credential Stealer and Backdoor
Every wheel of LiteLLM 1.107.0 on PyPI installs a credential stealer and a remote code execution backdoor. Both run each time Python starts. The code is not in the upstream GitHub source.
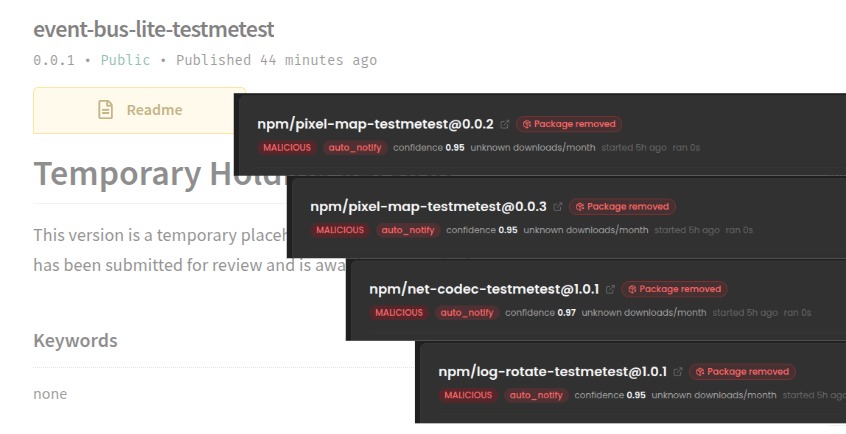
testmetest npm Packages Carry a Miasma-Family Worm
18 npm packages carry a Miasma-family worm that steals credentials, spreads to other packages and installs a wiper. New builds replace the binding.gyp trigger with a native addon.
Forged Commits Push a preinstall Dropper into hugo-paper and mevn-cli
An attacker pushed forged commits to the default branches of hugo-paper and mevn-cli. Running npm install or bun install in either repository downloads and runs a second-stage script from...

Ship Code.
Not Malware.
Start free with open source tools on your machine. Scale to a unified platform for your organization.
