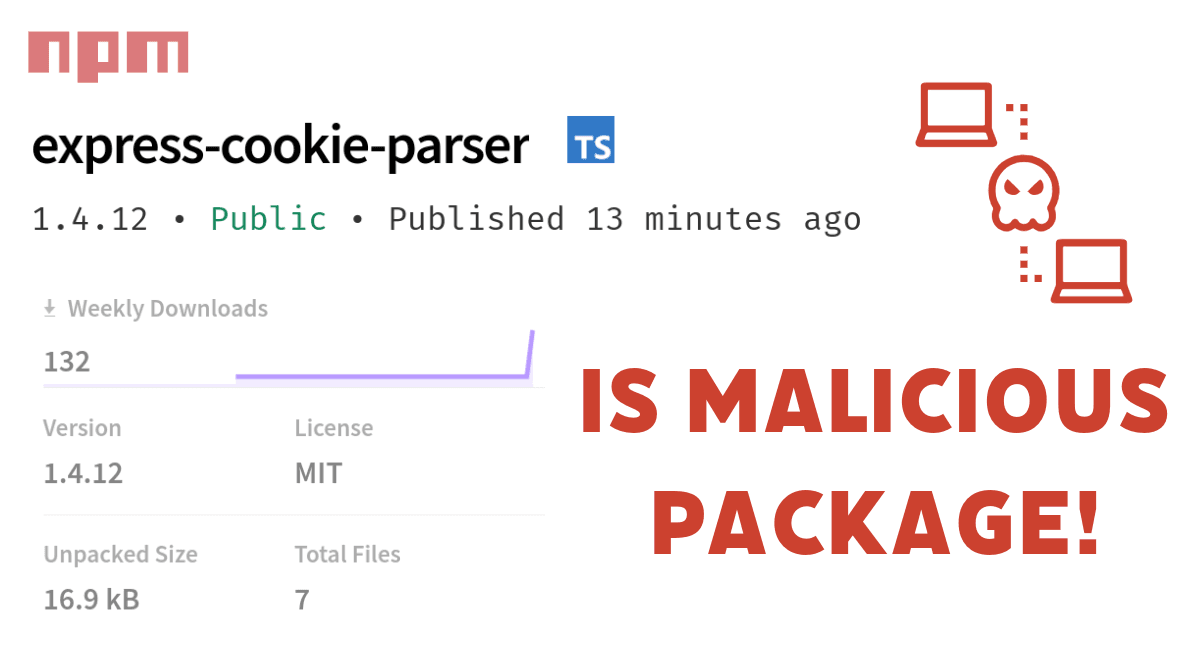
Malicious npm Package Impersonating Popular Express Cookie Parser
A malicious npm package impersonating the popular Express cookie parser package was discovered by SafeDep Cloud malicious package scanning service.
A malicious npm package impersonating the popular Express cookie parser package was discovered by SafeDep Cloud malicious package scanning service.
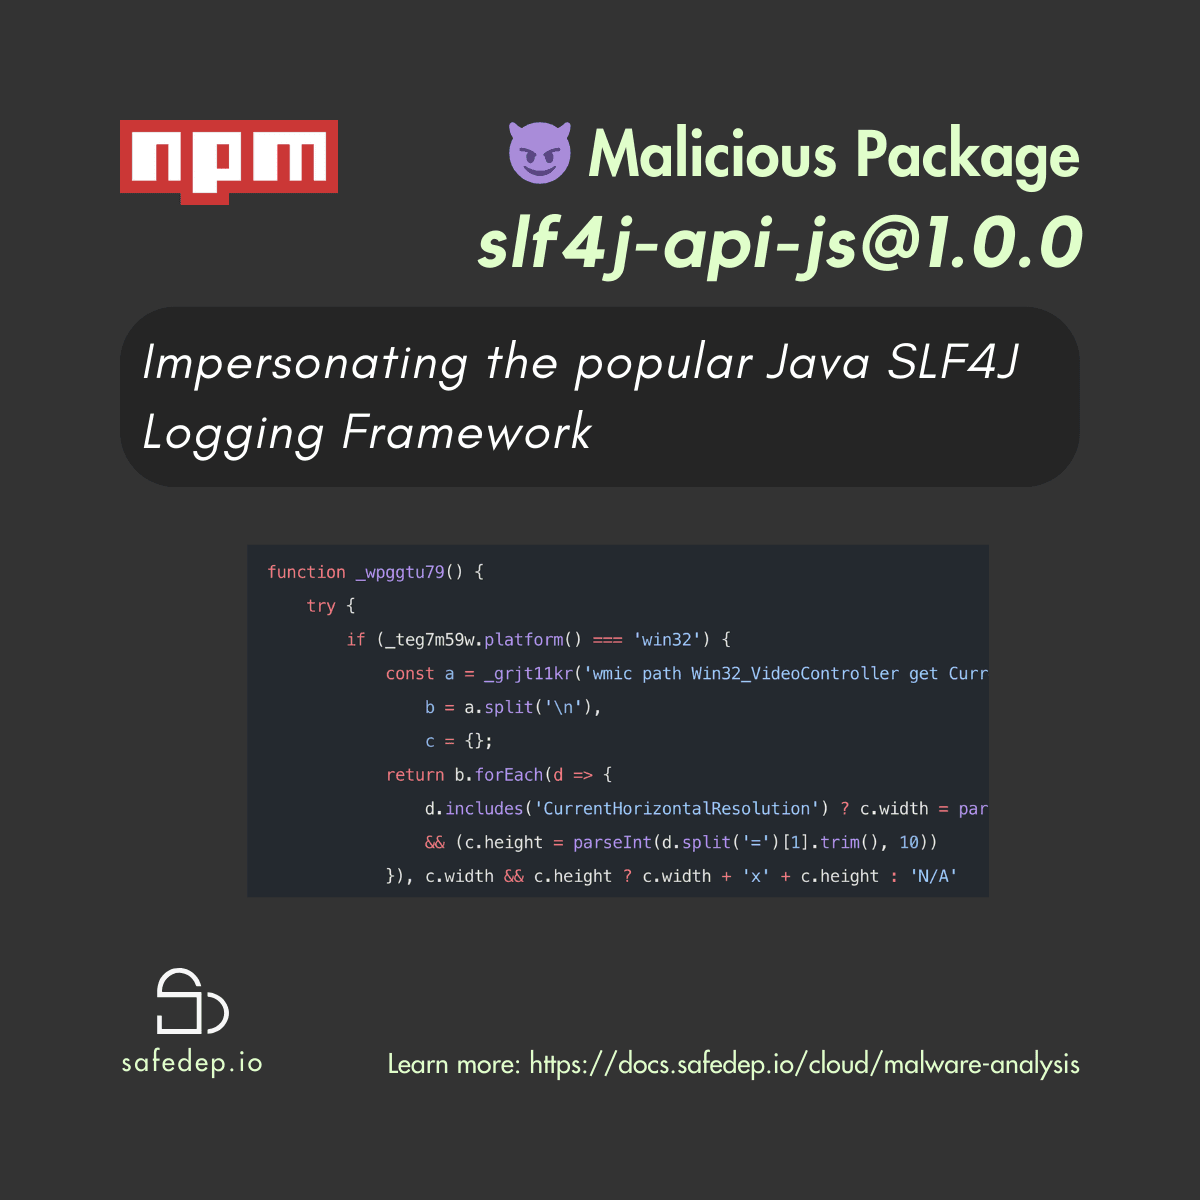
A malicious npm package impersonating the popular Java logging framework SLF4J is discovered by SafeDep Cloud malicious package scanning service.
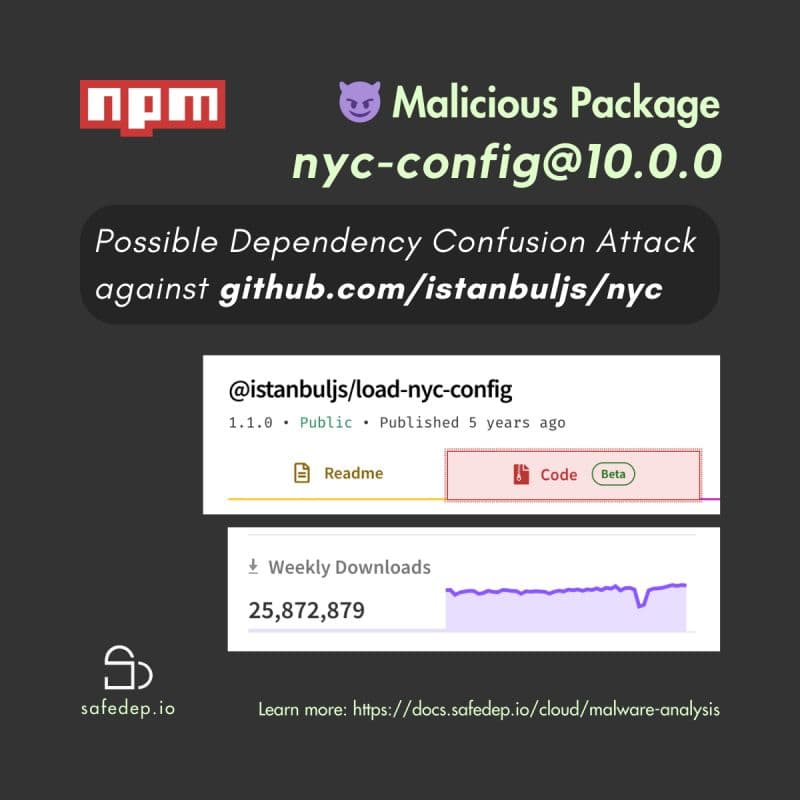
Possible typosquatting against @istanbuljs/load-nyc-config with ~25M weekly downloads.
Multiple npm packages impersonating popular package names were published to the npm registry including by a Snyk researcher apparently targeting internal packages at Cursor AI.
Multiple npm packages impersonating popular package names are being used to distribute malware. We take a closer look at the campaign.
