Behind the scenes
of SafeDep.
A continuously evolving engine built to protect modern software from malicious dependencies.
Ingesting the
open-source universe.

SafeDep continuously monitors public package registries like npm, PyPI, and RubyGems, pulling every new release the moment it appears. No blind spots. No delays. Every version is accounted for.

Three layers of analysis.
Zero trust assumptions.

Every package flows through SafeDep's multi-dimensional scanning pipeline. Three independent systems inspect the code from every angle—structural, behavioral, and pattern-driven.
AI Agent driving reasoning
that catches what scanners miss.
Beyond pattern matching, SafeDep's AI agent applies contextual reasoning to each package, analyzing code behavior, dependencies, and publishing patterns together.

From understanding the threat to stopping it.
Each verdict becomes part of SafeDep's threat registry, powering instant lookups through our API and automated protection inside your development and deployment workflows.
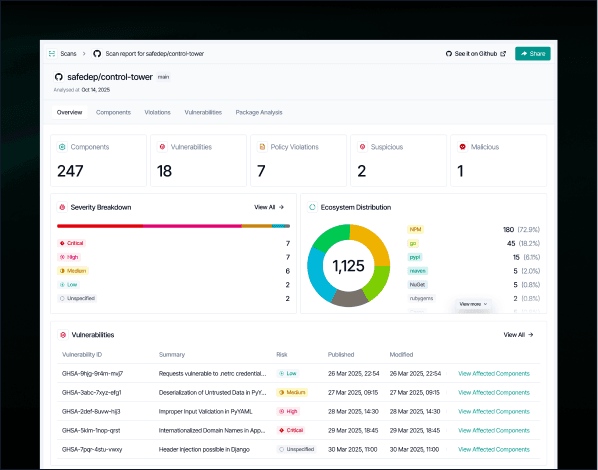
Stored Intelligence
Every detected malicious package is verified and added to SafeDep's continuously updated threat database.
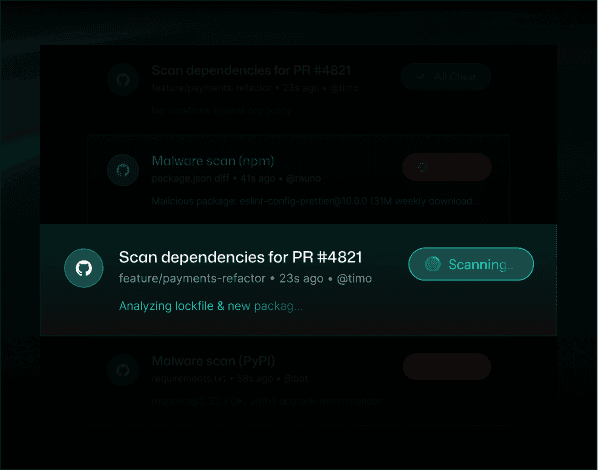
Automatic Defense
SafeDep applies this knowledge automatically inside your CI/CD to block malicious packages before they ship.
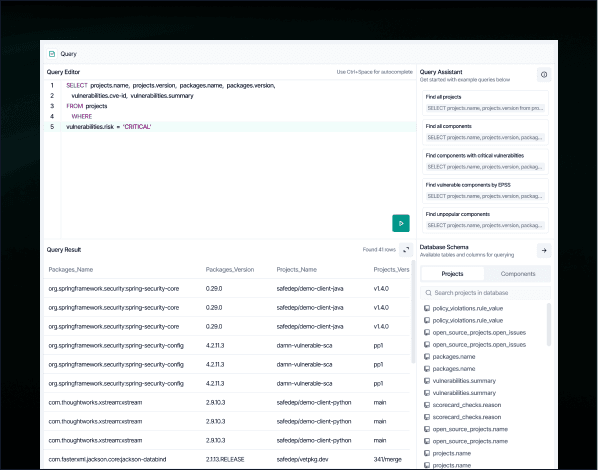
Query API
Access this intelligence instantly through a simple API to validate any dependency on demand.
Ship code
Not malware
Start free with open source tools on your machine. Scale to a unified platform for your organization.
