Multiple Malicious Python Packages Targeting Bittensor Crypto Developers
TL;DR
Multiple malicious Python packages targeting crypto developers and their applications were discovered on PyPI. The packages were used to steal funds by executing a stealthy staking operation. In this specific case, the attackers hooked a legitimate staking function to redirect the funds to their own wallet. The attack leveraged typosquatting to target the popular bittensor package.
Following malicious packages were disclosed by GitLab Vulnerability Research Team(opens in new tab):
bitensor@9.9.4bittenso-cli@9.9.4qbittensor@9.9.4bitensor@9.9.5bittenso@9.9.5
How SafeDep can protect developers?
SafeDep open source tools especially vet(opens in new tab) and pmg(opens in new tab) can help protect developers from malicious packages and other open source software supply chain attacks.
Our automated systems flagged the packages as suspicious due to multiple signals, including identifying the malicious code and intention in typosquatting packages. See example(opens in new tab)
- Hardcoded destination wallet address
5FjgkuPzAQHax3hXsSkNtue8E7moEYjTgrDDGxBvCzxc1nqR - Forced
transfer_all=Trueindicating operations without user consent
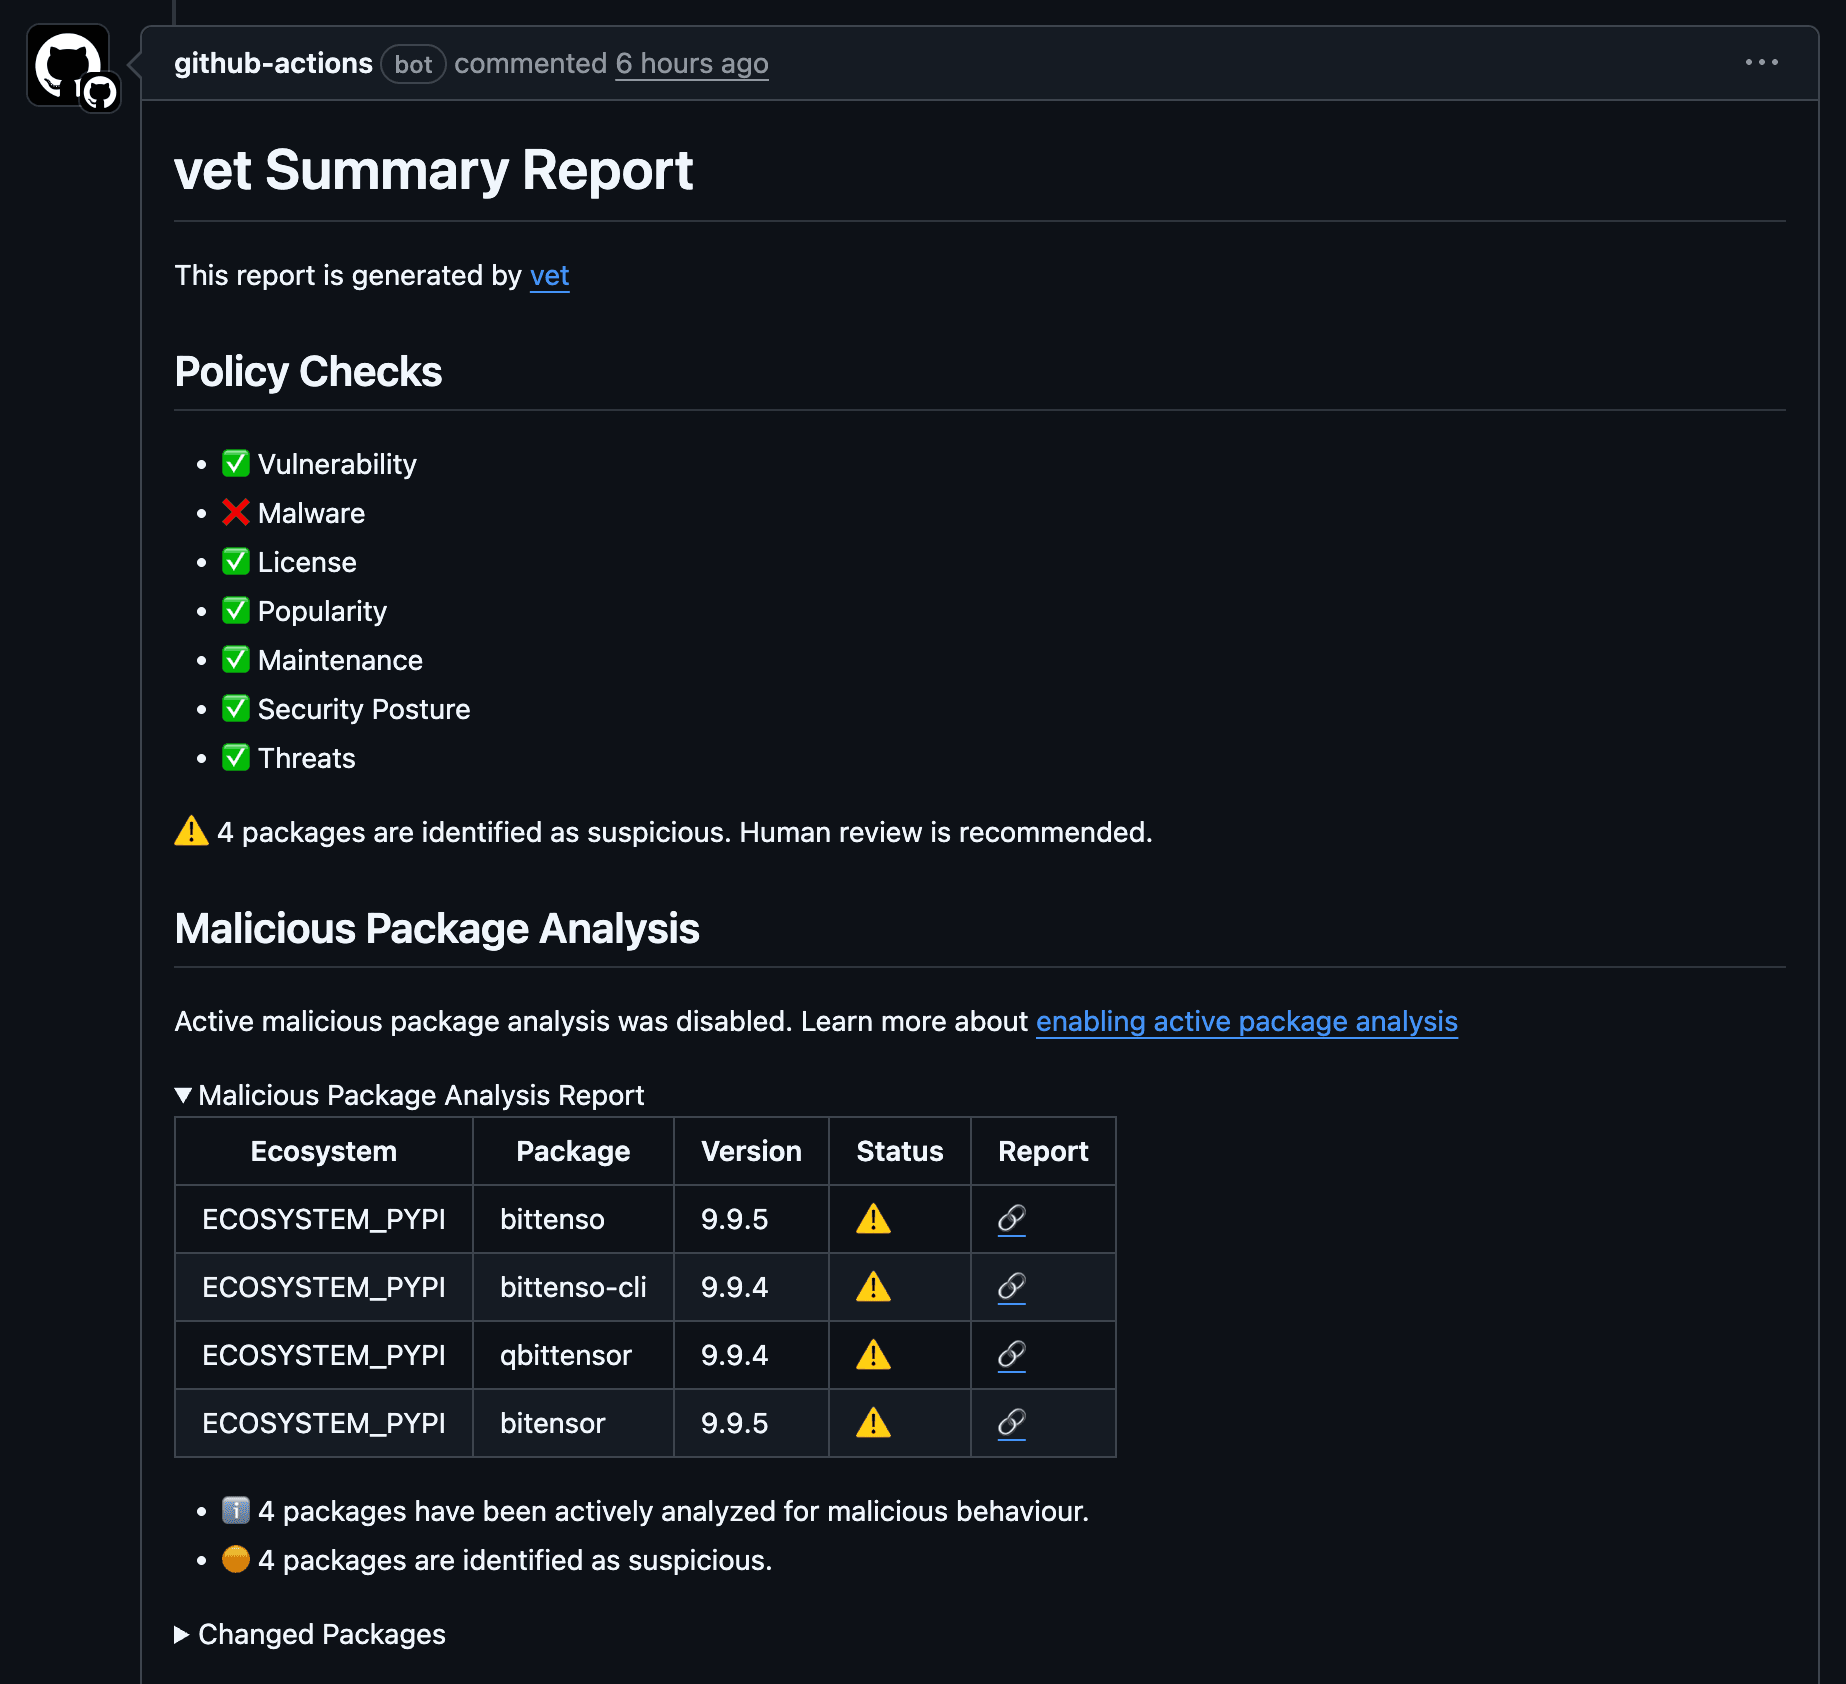
SafeDep vet(opens in new tab) alerted users in CI/CD pipelines when trying to add any of the compromised package through a PR.
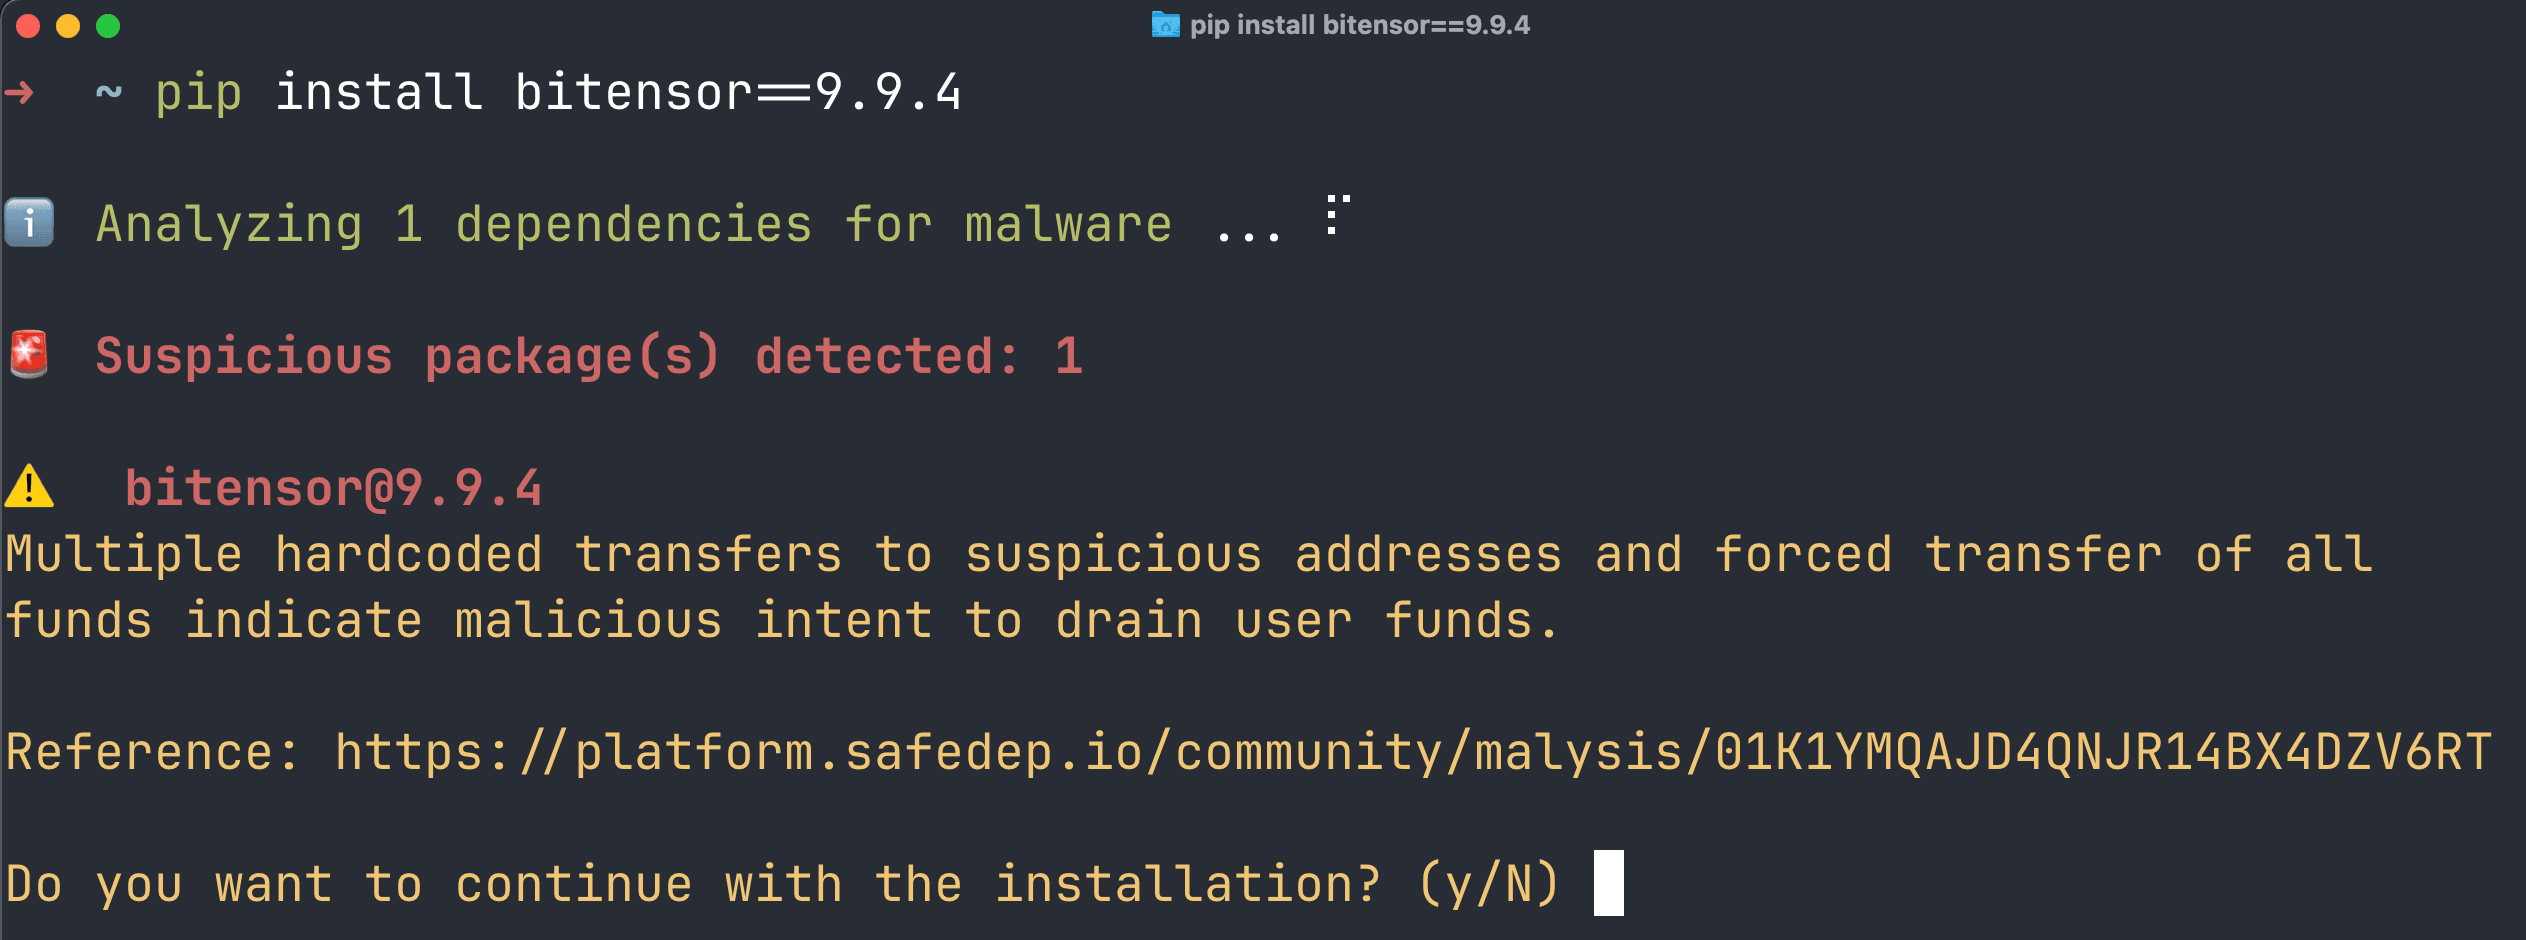
SafeDep pmg(opens in new tab) will alert developers when trying to install any of the compromised package.
How to protect your project?
At SafeDep, we believe code is the source of truth. We perform code analysis to detect vulnerabilities and malicious code in open source packages. If that is not feasible, general security best practices can be used to protect against common open source software supply chain attacks.
- Always vet open source packages for vulnerabilities and malicious code before use
- Ensure branch protection rules require code review before merging
- Establish trust on packages through its popularity, community or code review
- Avoid using most recently released package versions
- Prefer using open source packages only from trusted sources
SafeDep vet(opens in new tab) seamlessly integrates with your CI/CD pipeline and alerts you when trying to add any of the compromised package through a PR. SafeDep pmg(opens in new tab) will alert developers when trying to install any of the compromised package.
References
- pypi
- oss
- malware
- crypto


