Ship Code. Not Malware. SafeDep Launches GitHub App for Malicious Package Protection
Malicious Package in the Wild
The recent supply chain attack targeting the npm ecosystem, such as the Shai-Hulud and the S1ngularity campaign, has raised serious concerns among the developer and security engineering community. Detecting malicious code in open source packages is a complex problem, and it requires a multi-layered approach. We have been doing this for a while leveraging:
While we handle the complexity, we have always strived to provide the simplest and minimally intrusive solution to protect developers from malicious packages. So we launched SafeDep GitHub App(opens in new tab) to make it ridiculously simple to protect your code repositories from malicious packages.
Installation is simple and zero configuration - Install Now(opens in new tab)
Zero Configuration Malicious Package Protection
How To Get Started?
- Install the SafeDep GitHub App(opens in new tab)
- Wait for the next pull request to be scanned
- Stay protected from malicious packages
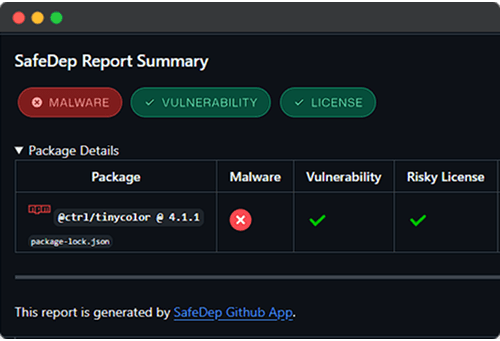
That’s it! It is really that simple. Here is how it looks like in action:
How it works?
SafeDep scans all open source packages released to supported registries such as npm, PyPI, RubyGems, Cargo and more. SafeDep applies static, dynamic and agentic analysis to detect malicious packages. While these packages are removed from the registries, SafeDep tools leverage this threat intelligence to protect code repositories from malicious packages.
What are the benefits?
- Zero Configuration: Install the app with zero configuration
- Real-time Protection: Scans every pull request for malicious packages
- Multi-Ecosystem: Supports npm, pnpm, yarn, and more
- Multi-Language: Supports JavaScript, TypeScript, Python, and more
- Multi-Platform: Supports Windows, Linux, and macOS
Documentation and Support
- GitHub App Documentation: SafeDep GitHub App(opens in new tab)
- Community support: https://docs.safedep.io/community(opens in new tab)
- npm
- oss
- malware
- supply-chain


