


Deep-Live-Cam Supply Chain Attack: Technical Analysis
A malicious dependency in Deep-Live-Cam loads a clipboard hijacker. We trace the installation trigger, Telegraph delivery, and Windows and macOS persistence.
A malicious dependency in Deep-Live-Cam loads a clipboard hijacker. We trace the installation trigger, Telegraph delivery, and Windows and macOS persistence.
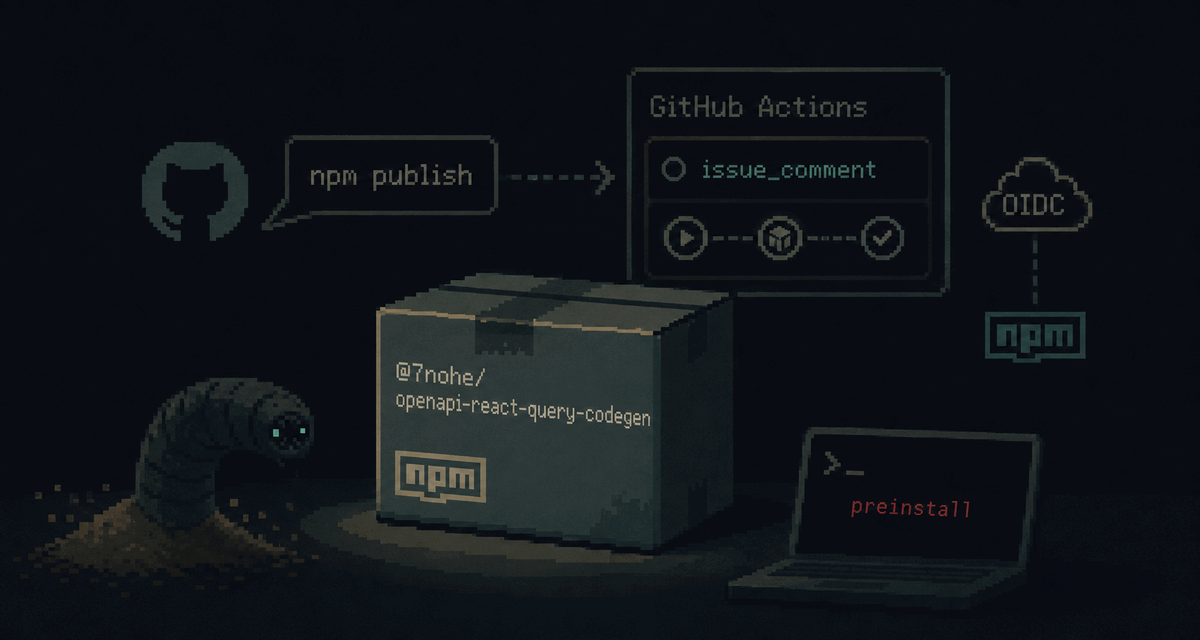
An attacker exploited a flawed GitHub Actions workflow to publish 10 malicious versions of @7nohe/openapi-react-query-codegen (671K downloads/month) via npm OIDC trusted publishing. The payload uses...
A compromised release of the popular Rust crate arrayref pulled in a typosquatted proc-macro1 whose build script downloads and runs a remote binary at compile time. The malicious versions are now...
ulid-xyz is a remote access trojan we reported to OSV as MAL-2026-6672. It reached developers as a third-level transitive dependency of ioredis-xyz, a copy of the real Redis client planted in 28...
A YouTube video ad impersonating TradingView delivered a fake .pkg installer. Inside: a self-healing LaunchAgent, an AES-encrypted V8 bytecode payload, and a Node.js MITM proxy trusted by a rogue...
SafeDep keeps analytics anonymous and cookie-free until you opt in. Accepting helps us understand product usage and improve your experience. Privacy Policy
Choose what you share. You can change this anytime from the footer.
