


On this page
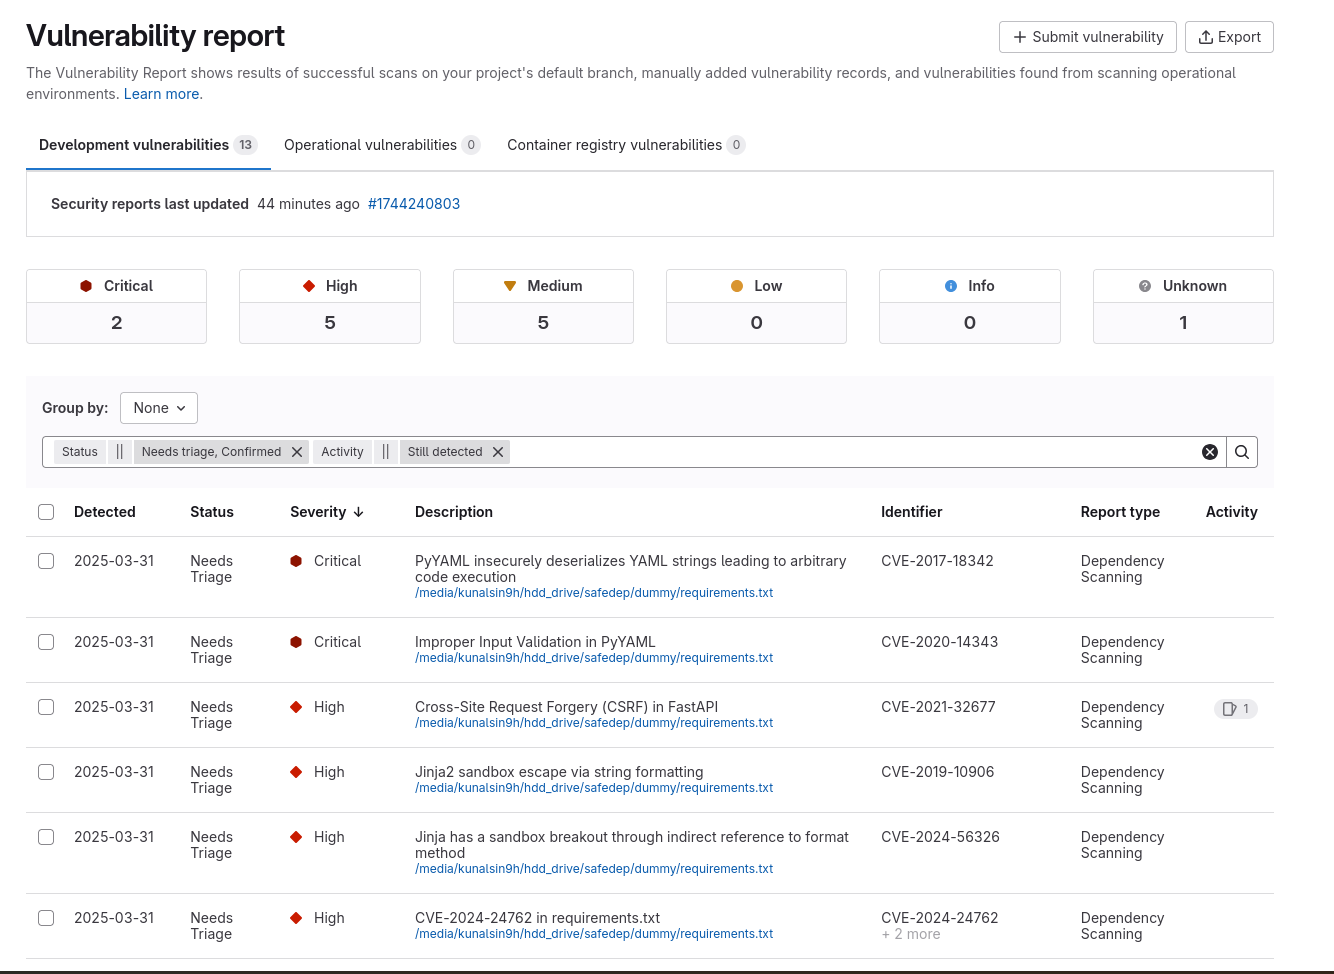
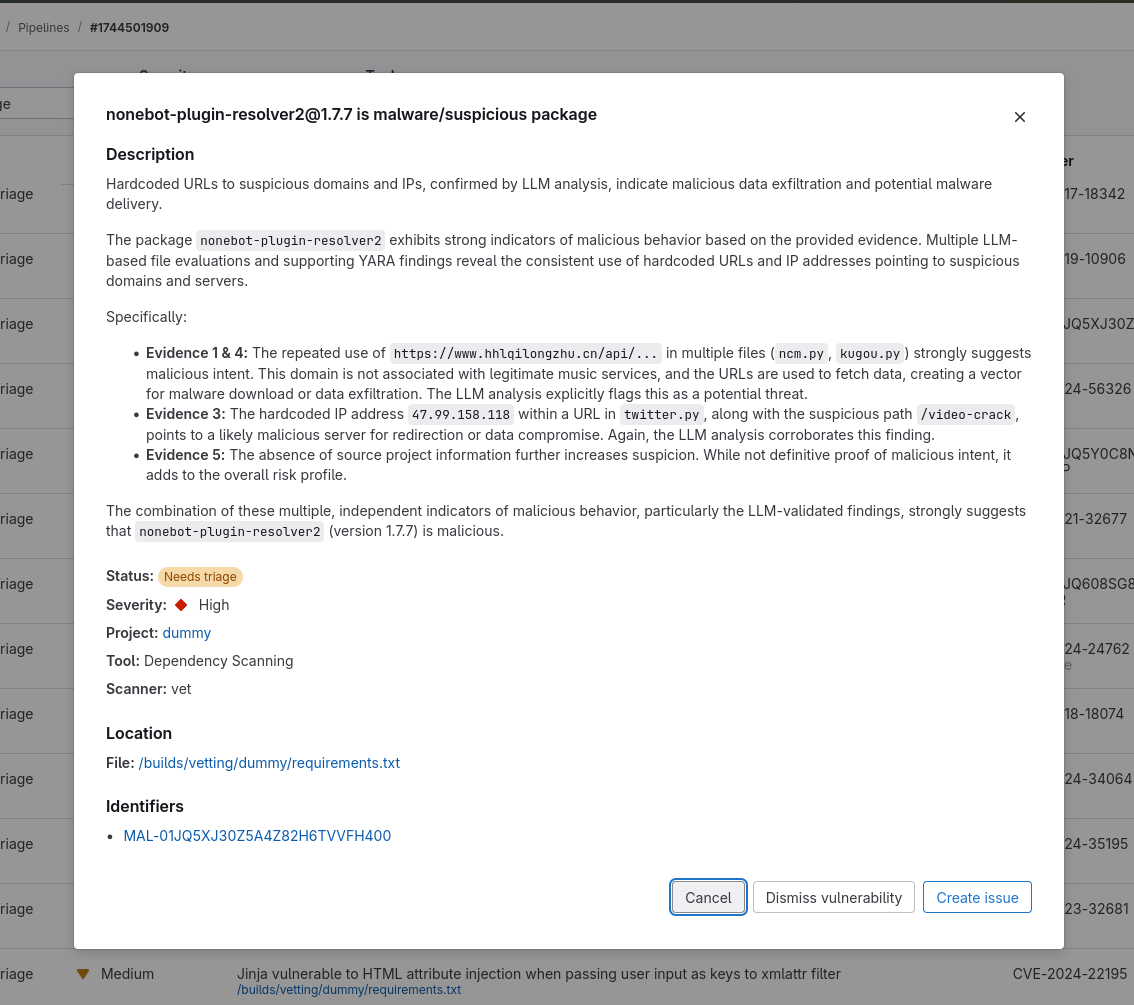
Announcing the new GitLab CI/CD Component, available in GitLab CI Catalog for seamless integration of vet in GitLab CI. Protect against vulnerable and malicious packages in your GitLab projects. This integration enables GitLab users to easily integrate vet with their GitLab CI pipelines. This integration protects GitLab projects from vulnerable and malicious packages in the dependency tree.
TL;DR
Usage
Features
- Scan all dependencies and report vulnerabilities to GitLab security dashboard
- Integrates with SafeDep Cloud to protect against malicious open source packages through active code analysis
Support
- Report bugs and feature requests to GitHub issues
- Start feature discussions at GitHub discussions
- gitlab
- cicd
- integration
- malware
Author

SafeDep Team
safedep.io
Share
The Latest from SafeDep blogs
Follow for the latest updates and insights on open source security & engineering
Introducing SafeDep Threat Intel
SafeDep Threat Intel gives SOC and cyber defense teams the malicious package intelligence behind SafeDep's platform, to query or to push into the tools they already run.
Mini Shai-Hulud Strikes Again: openapi-react-query-codegen
An attacker exploited a flawed GitHub Actions workflow to publish 10 malicious versions of @7nohe/openapi-react-query-codegen (671K downloads/month) via npm OIDC trusted publishing. The payload uses...
A malicious npm package hidden three dependencies deep: the ulid-xyz delivery chain
ulid-xyz is a remote access trojan we reported to OSV as MAL-2026-6672. It reached developers as a third-level transitive dependency of ioredis-xyz, a copy of the real Redis client planted in 28...
From YouTube Ad to Root: How a Fake TradingView Installer Delivers a macOS Stealer
A YouTube video ad impersonating TradingView delivered a fake .pkg installer. Inside: a self-healing LaunchAgent, an AES-encrypted V8 bytecode payload, and a Node.js MITM proxy trusted by a rogue...

Ship Code.
Not Malware.
Start free with open source tools on your machine. Scale to a unified platform for your organization.
