


Ship Code. Not Malware. SafeDep Launches GitHub App for Malicious Package Protection
On this page
Malicious Package in the Wild
The recent supply chain attack targeting the npm ecosystem, such as the Shai-Hulud and the S1ngularity campaign, has raised serious concerns among the developer and security engineering community. Detecting malicious code in open source packages is a complex problem, and it requires a multi-layered approach. We have been doing this for a while leveraging:
While we handle the complexity, we have always strived to provide the simplest and minimally intrusive solution to protect developers from malicious packages. So we launched SafeDep GitHub App to make it ridiculously simple to protect your code repositories from malicious packages.
Installation is simple and zero configuration - Install Now
Zero Configuration Malicious Package Protection
How To Get Started?
- Install the SafeDep GitHub App
- Wait for the next pull request to be scanned
- Stay protected from malicious packages
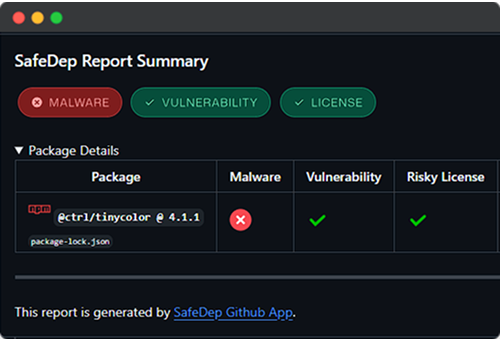
That’s it! It is really that simple. Here is how it looks like in action:
How it works?
SafeDep scans all open source packages released to supported registries such as npm, PyPI, RubyGems, Cargo and more. SafeDep applies static, dynamic and agentic analysis to detect malicious packages. While these packages are removed from the registries, SafeDep tools leverage this threat intelligence to protect code repositories from malicious packages.
What are the benefits?
- Zero Configuration: Install the app with zero configuration
- Real-time Protection: Scans every pull request for malicious packages
- Multi-Ecosystem: Supports npm, pnpm, yarn, and more
- Multi-Language: Supports JavaScript, TypeScript, Python, and more
- Multi-Platform: Supports Windows, Linux, and macOS
Documentation and Support
- GitHub App Documentation: SafeDep GitHub App
- Community support: https://docs.safedep.io/community
- npm
- oss
- malware
- supply-chain
Author

SafeDep Team
safedep.io
Share
The Latest from SafeDep blogs
Follow for the latest updates and insights on open source security & engineering
eMudhra CA Key Compromise: Response Guide for Developers
Anyone can compute eight eMudhra intermediate CA private keys from public certificates. Browsers block the compromised intermediates, but CI runners, containers, JVMs and Go binaries can still trust...

Compromised LiteLLM 1.107.0 on PyPI Installs a Credential Stealer and Backdoor
Every wheel of LiteLLM 1.107.0 on PyPI installs a credential stealer and a remote code execution backdoor. Both run each time Python starts. The code is not in the upstream GitHub source.
testmetest npm Packages Carry a Miasma-Family Worm
18 npm packages carry a Miasma-family worm that steals credentials, spreads to other packages and installs a wiper. New builds replace the binding.gyp trigger with a native addon.
Forged Commits Push a preinstall Dropper into hugo-paper and mevn-cli
An attacker pushed forged commits to the default branches of hugo-paper and mevn-cli. Running npm install or bun install in either repository downloads and runs a second-stage script from...

Ship Code.
Not Malware.
Start free with open source tools on your machine. Scale to a unified platform for your organization.
