


AI Agent Cline v2.3.0 Compromised: From Prompt Injection to Unauthorized npm Publish
On this page
TL;DR
On February 17, 2026, a compromised npm token was used to publish an unauthorized version of the popular AI coding tool, cline@2.3.0. The version contained a modified package.json with a postinstall script that silently installed another package globally.
What Happened?
According to the GitHub Security Advisory GHSA-9ppg-jx86-fqw7, an unauthorized party gained access to an npm publish token and released cline@2.3.0. The malicious version was live for roughly 8 hours (3:26 AM to 11:30 AM PT on February 17) before being deprecated.
Security researcher Adnan Khan’s investigation identified a prompt injection vulnerability in Cline’s AI-powered issue triage workflow. The workflow used claude-code-action with broad tool permissions (Bash, Write, Edit) and allowed any GitHub user to trigger it by opening an issue. A crafted issue title could inject a prompt that tricks Claude into running npm install from an attacker-controlled fork. Because the triage workflow shared GitHub Actions cache scope with Cline’s nightly publish workflow, this could be chained with cache poisoning to exfiltrate publication secrets (NPM_RELEASE_TOKEN, VS Code Marketplace, and OpenVSX credentials). The exact method of token theft has not been publicly confirmed. Notably, these tokens were scoped to publisher identity rather than individual extensions, meaning nightly credentials could publish production releases.
What Does the Payload Do?
The postinstall script was:
"postinstall": "npm install -g openclaw@latest"
OpenClaw is a legitimate, non-malicious open-source project. The payload did not steal credentials, install backdoors, or exfiltrate data. This looks like a proof of concept: someone demonstrating the attack’s feasibility rather than deploying an operational payload. The same postinstall hook could have delivered a credential stealer or reverse shell to every developer who ran npm install -g cline@2.3.0. The mechanism was proven, even if the payload was benign.
The Diff
The only change between the legitimate 2.2.3 (which 2.3.0 was based on) and the compromised version was in the package.json.
Index: package/package.json===================================================================--- package/package.json+++ package/package.json@@ -1,7 +1,7 @@ { "name": "cline",- "version": "2.2.3",+ "version": "2.3.0", "description": "Autonomous coding agent CLI - capable of creating/editing files, running commands, using the browser, and more", "main": "dist/cli.mjs", "bin": { "cline": "./dist/cli.mjs"@@ -31,9 +31,10 @@ "typecheck": "npx tsc --noEmit", "link": "npm run build && npm link", "unlink": "npm unlink -g cline", "test": "vitest",- "test:run": "vitest run"+ "test:run": "vitest run",+ "postinstall": "npm install -g openclaw@latest" }, "keywords": [ "cline", "claude",All other files, including the CLI binary dist/cli.mjs, were identical to the previous version.
How PMG Flagged It
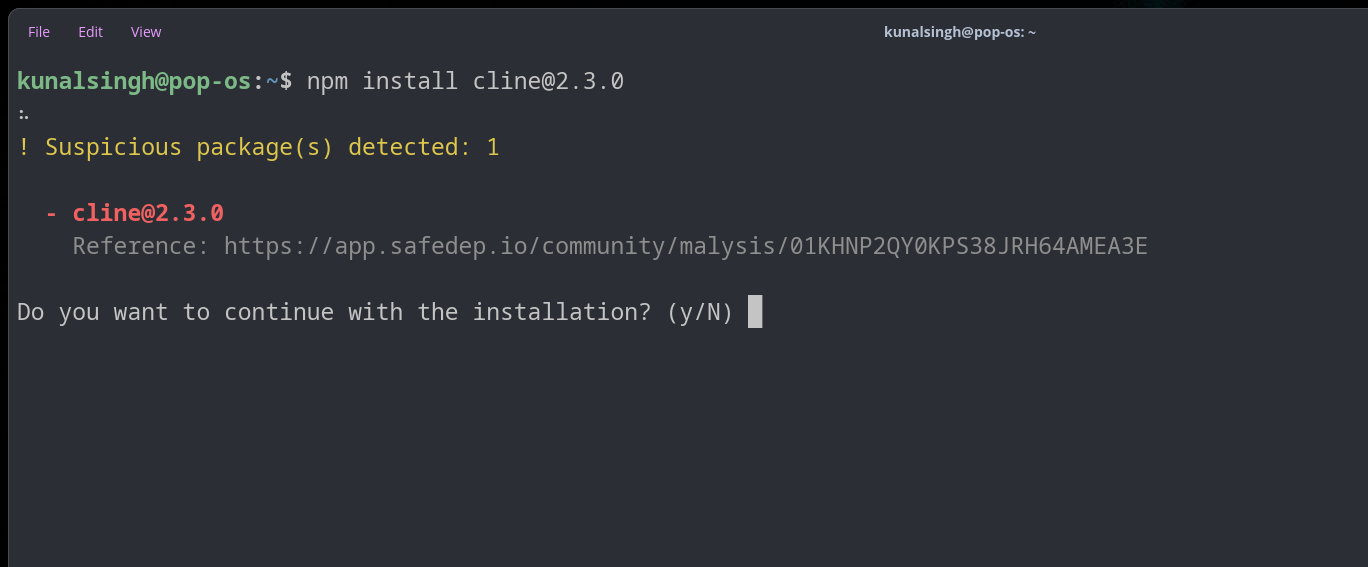
SafeDep Package Manager Guard (PMG) flagged cline@2.3.0 as suspicious during installation:
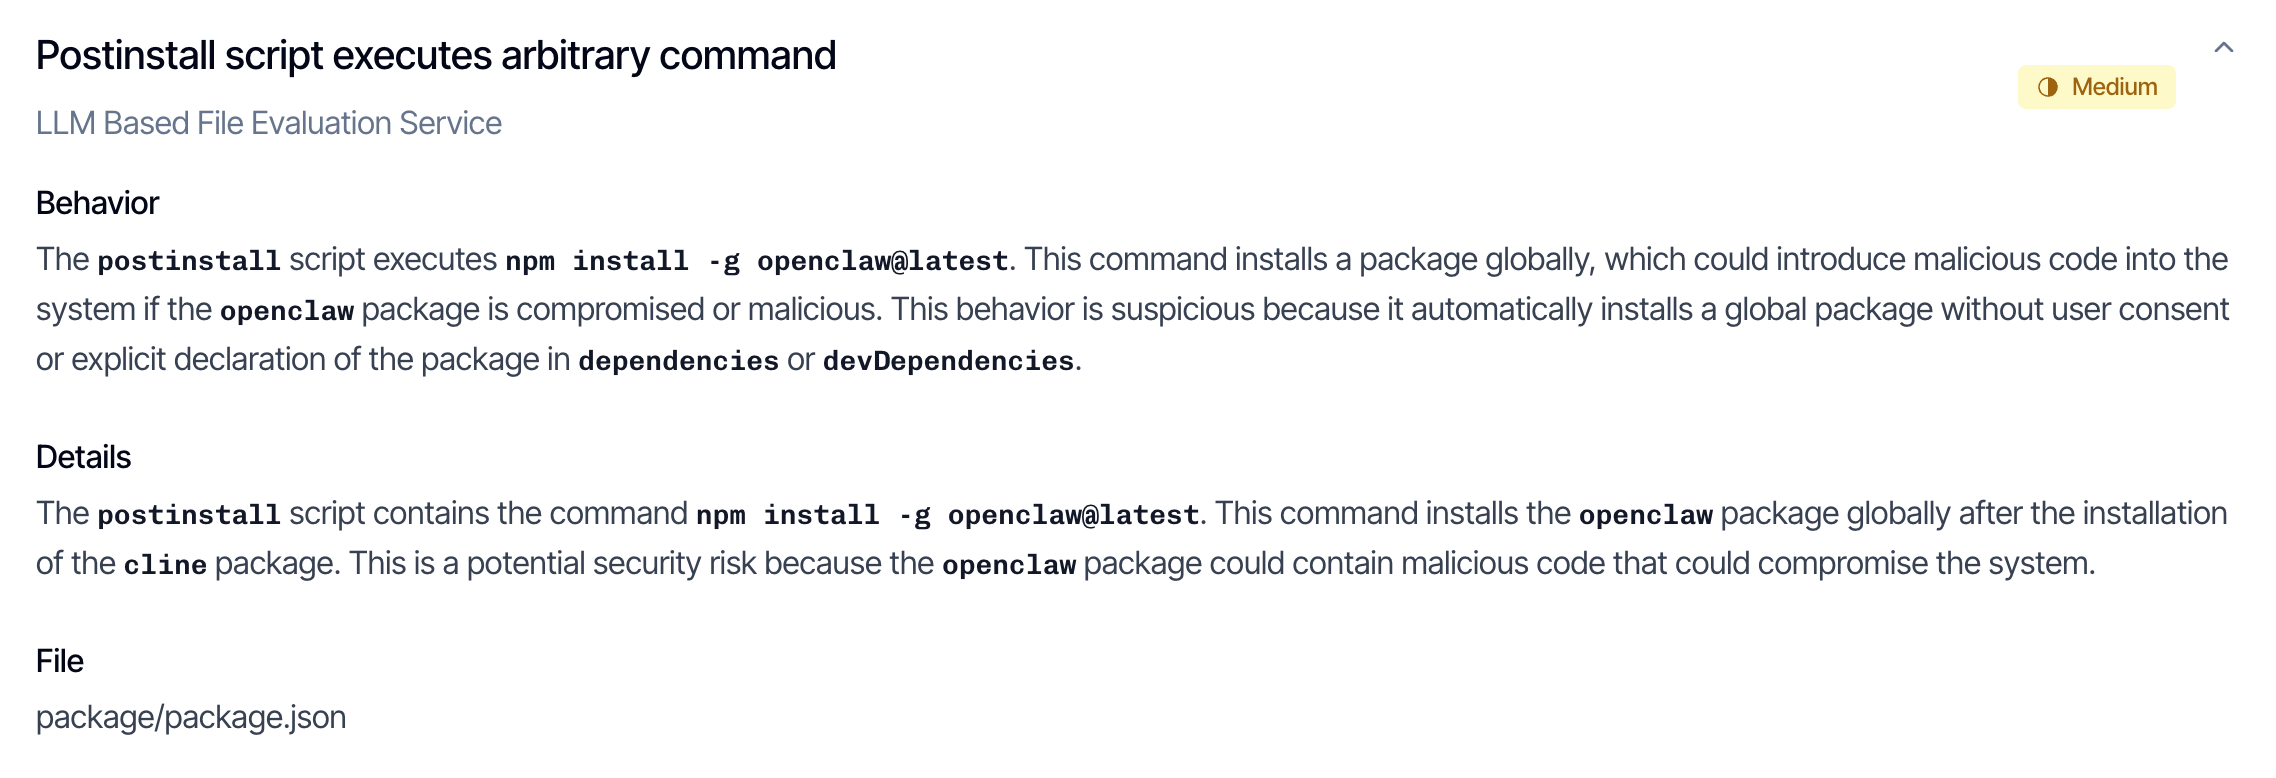
SafeDep’s LLM-based file evaluation identified the postinstall script as executing an arbitrary command, installing a global package without user consent or explicit declaration in dependencies:
Users of pmg would have been blocked or alerted during the attempted installation, preventing the payload from executing.
For teams looking to catch malicious dependencies earlier in the development lifecycle, the SafeDep GitHub App can flag pull requests that introduce known malicious packages before they reach installation.
Post-Incident Response
Cline revoked the compromised token, removed the vulnerable AI triage workflow (PR #9211), and moved npm publishing to OIDC provenance via GitHub Actions. This eliminates long-lived static tokens as an attack surface for future publishes.
Next Steps for Users
If you installed cline@2.3.0 between 3:26 AM PT and 11:30 AM PT on February 17:
- Update:
npm install -g cline@latest(version2.4.0or higher) - Cleanup: Remove
openclawif you didn’t intend to install it:npm uninstall -g openclaw
References
- npm
- oss
- malware
- cline
- supply-chain
- prompt-injection
Author
Kunal Singh
safedep.io
Share
The Latest from SafeDep blogs
Follow for the latest updates and insights on open source security & engineering
eMudhra CA Key Compromise: Response Guide for Developers
Anyone can compute eight eMudhra intermediate CA private keys from public certificates. Browsers block the compromised intermediates, but CI runners, containers, JVMs and Go binaries can still trust...

Compromised LiteLLM 1.107.0 on PyPI Installs a Credential Stealer and Backdoor
Every wheel of LiteLLM 1.107.0 on PyPI installs a credential stealer and a remote code execution backdoor. Both run each time Python starts. The code is not in the upstream GitHub source.
testmetest npm Packages Carry a Miasma-Family Worm
18 npm packages carry a Miasma-family worm that steals credentials, spreads to other packages and installs a wiper. New builds replace the binding.gyp trigger with a native addon.
Forged Commits Push a preinstall Dropper into hugo-paper and mevn-cli
An attacker pushed forged commits to the default branches of hugo-paper and mevn-cli. Running npm install or bun install in either repository downloads and runs a second-stage script from...

Ship Code.
Not Malware.
Start free with open source tools on your machine. Scale to a unified platform for your organization.
