


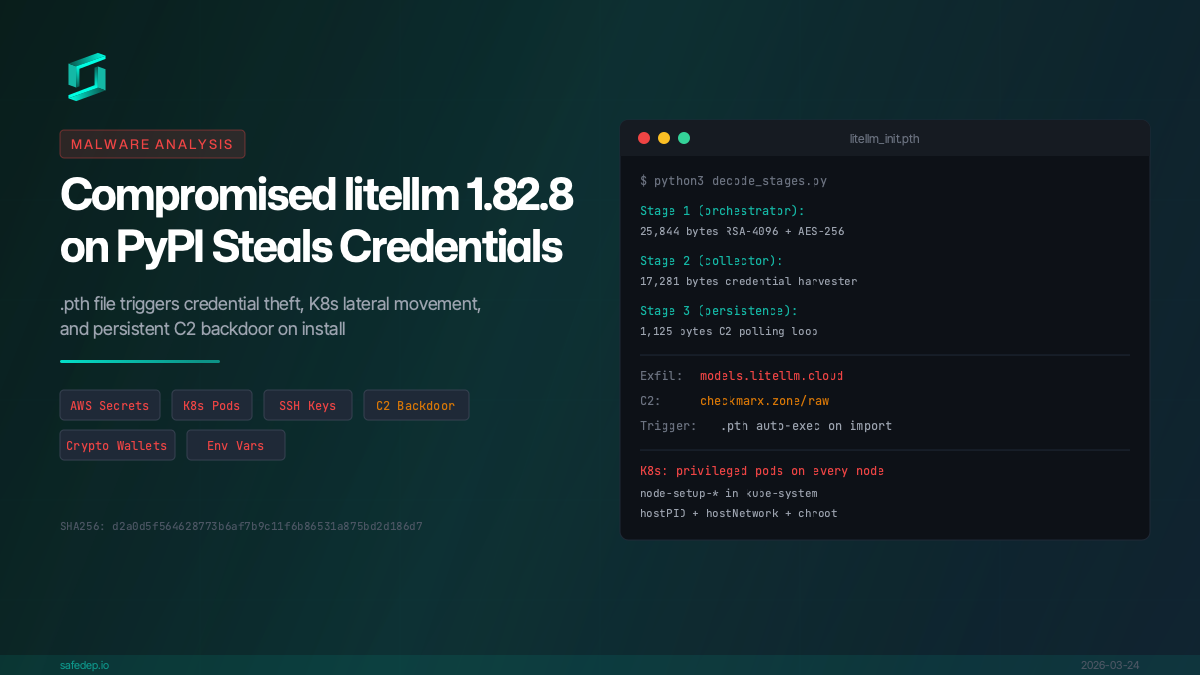
Malicious litellm 1.82.8: Credential Theft and Persistent Backdoor
Analysis of compromised litellm 1.82.8 on PyPI: a .pth file triggers credential theft, AWS/K8s secret exfiltration, and persistent C2 backdoor on install.
Analysis of compromised litellm 1.82.8 on PyPI: a .pth file triggers credential theft, AWS/K8s secret exfiltration, and persistent C2 backdoor on install.
Analysis of malicious open source packages from Datadog's malicious packages dataset. Each of these packages were found in the wild and confirmed to be malicious. The goal of this analysis is to...
Multiple malicious Python packages targeting crypto developers and their applications using typosquatting were discovered on PyPI. The packages were used to steal funds by executing a stealthy...
SafeDep keeps analytics anonymous and cookie-free until you opt in. Accepting helps us understand product usage and improve your experience. Privacy Policy
Choose what you share. You can change this anytime from the footer.
