


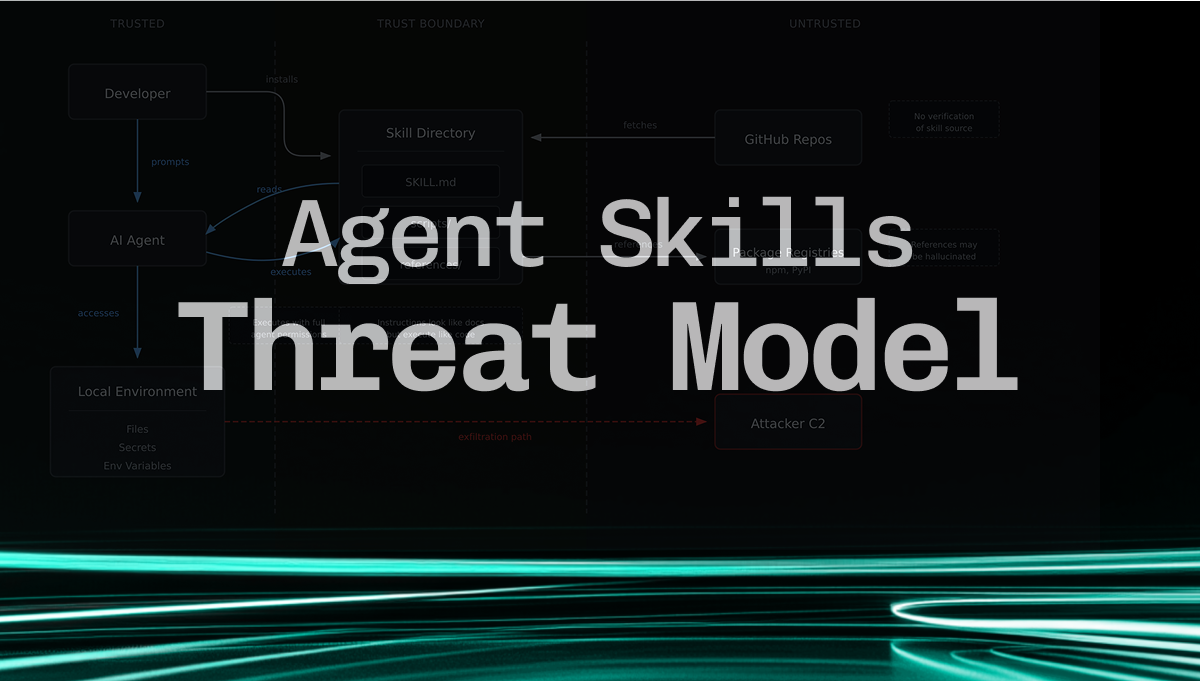
Agent Skills Threat Model
Discover critical security threats in Agent Skills - Anthropic's open format for AI agent capabilities. Learn about supply chain attacks, deferred code execution, prompt injection, and multiple...
Discover critical security threats in Agent Skills - Anthropic's open format for AI agent capabilities. Learn about supply chain attacks, deferred code execution, prompt injection, and multiple...
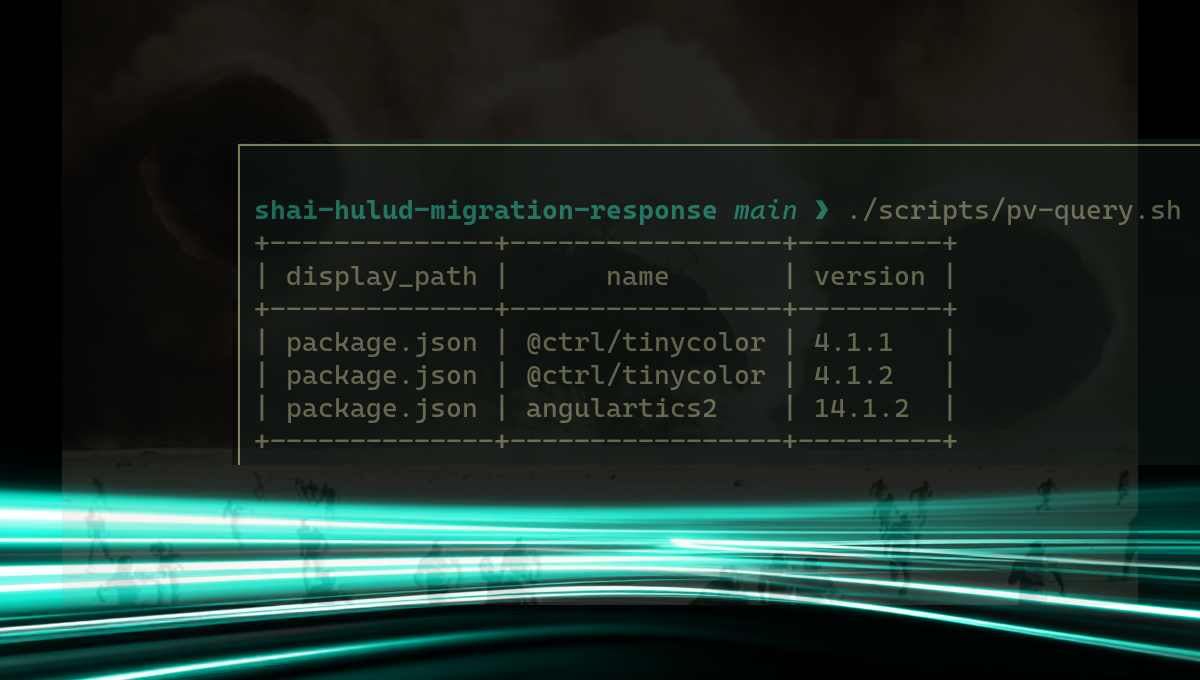
The Shai-Hulud supply chain attack is a major incident targeting developers through malicious packages in the npm ecosystem. This post outlines the incident response steps that can be taken to...
Modern software rarely ships as a single, hand-crafted binary. Instead, it is assembled from hundreds, sometimes thousands of third-party components that evolve on their own schedule. Knowing exactly...
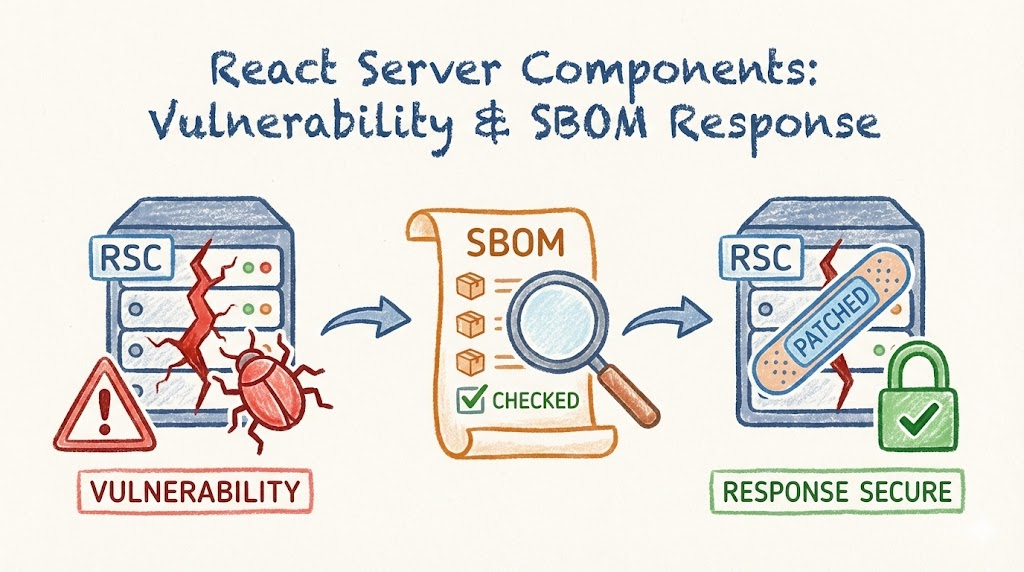
A critical pre-authenticated remote code execution vulnerability (CVE-2025-55182) was disclosed in React Server Components, affecting Next.js applications using the App Router. Learn about the...
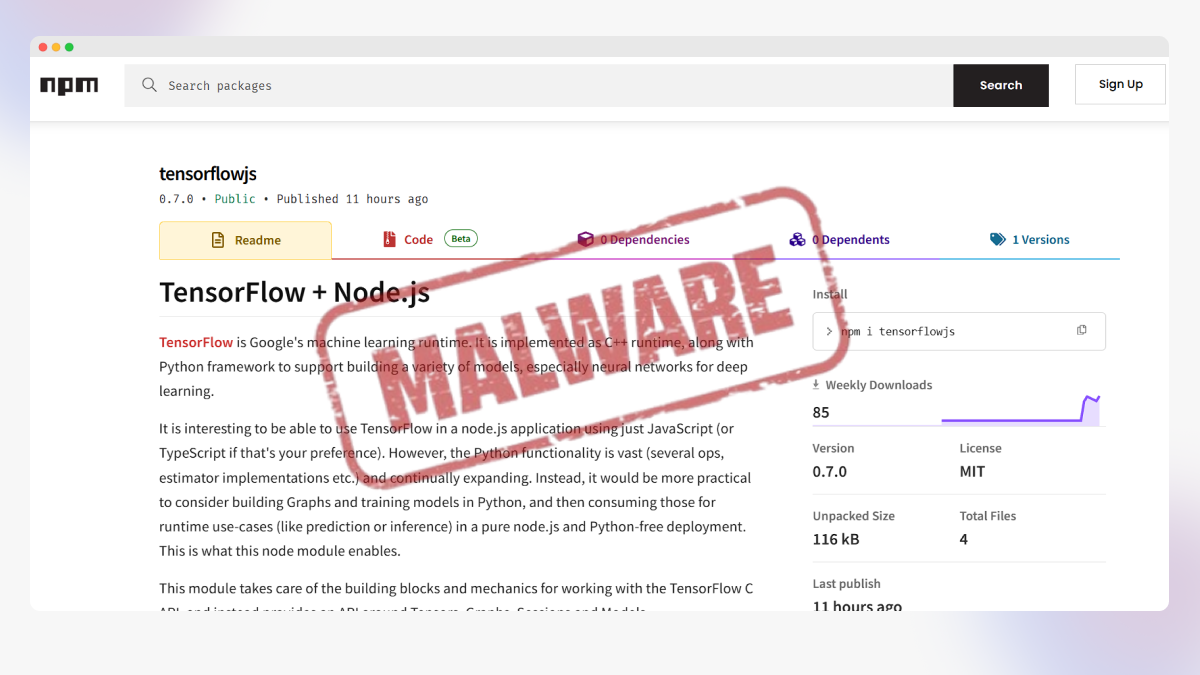
A malicious NPM package targeting TensorFlow users was discovered on npm. The package uses typosquatting to target the popular `tensorflow` package.
SafeDep keeps analytics anonymous and cookie-free until you opt in. Accepting helps us understand product usage and improve your experience. Privacy Policy
Choose what you share. You can change this anytime from the footer.
