


The State of MCP Registries
Explore the architecture of the Model Context Protocol (MCP) and the state of its official registry. Learn how to consume server packages programmatically and discover the underlying challenges of...
Explore the architecture of the Model Context Protocol (MCP) and the state of its official registry. Learn how to consume server packages programmatically and discover the underlying challenges of...
Critical npm supply chain attack compromises zapier-sdk, @asyncapi, posthog, and @postman packages with self-replicating malware. Technical analysis reveals credential harvesting, GitHub Actions...
Diff-based Software Composition Analysis (SCA) scanners in pull requests are prone to blind spots. By relying only on git diff data, they miss package context, suffer from nondeterministic...
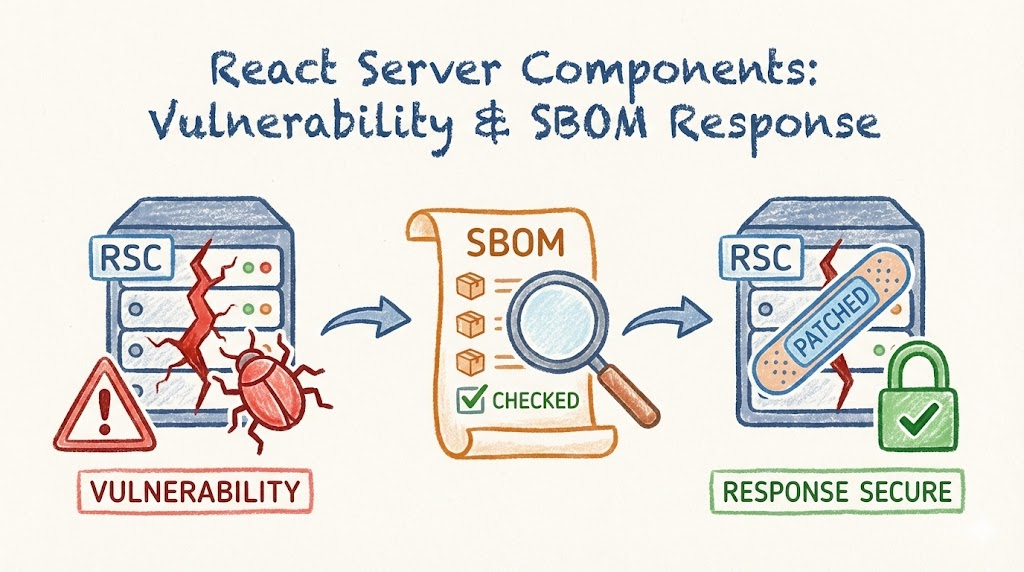
A critical pre-authenticated remote code execution vulnerability (CVE-2025-55182) was disclosed in React Server Components, affecting Next.js applications using the App Router. Learn about the...
The Shai-Hulud supply chain attack is a major incident targeting developers through malicious packages in the npm ecosystem. This post outlines the incident response steps that can be taken to...
SafeDep keeps analytics anonymous and cookie-free until you opt in. Accepting helps us understand product usage and improve your experience. Privacy Policy
Choose what you share. You can change this anytime from the footer.
