


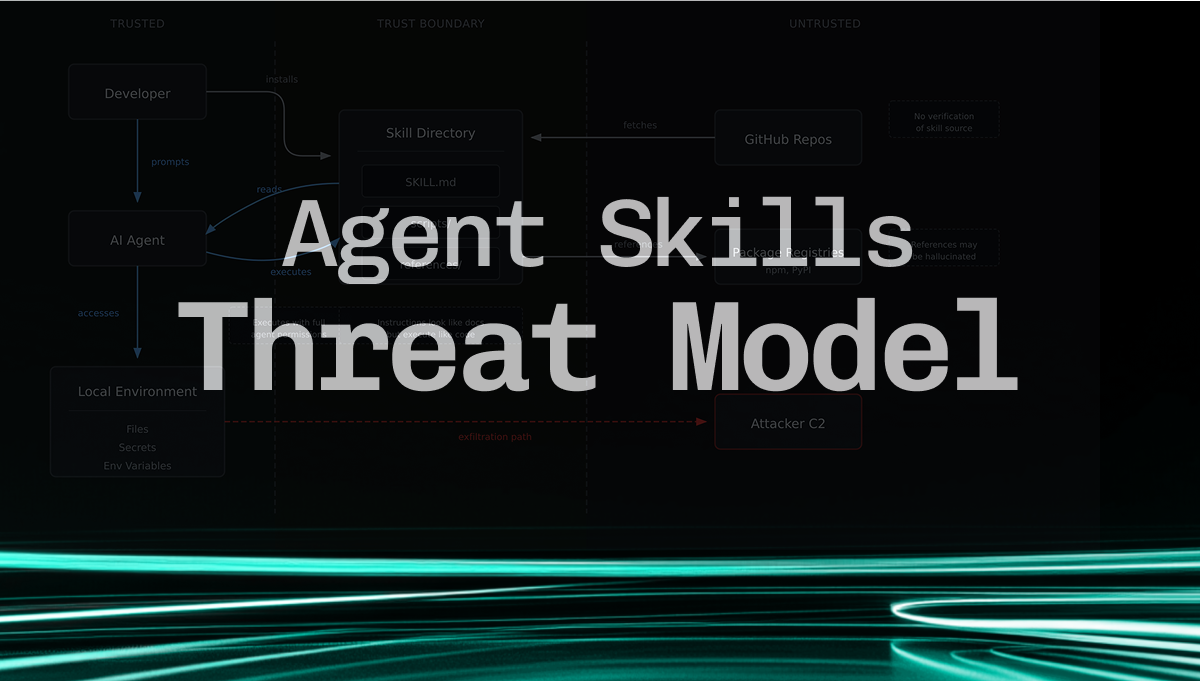
Agent Skills Threat Model
Discover critical security threats in Agent Skills - Anthropic's open format for AI agent capabilities. Learn about supply chain attacks, deferred code execution, prompt injection, and multiple...
Discover critical security threats in Agent Skills - Anthropic's open format for AI agent capabilities. Learn about supply chain attacks, deferred code execution, prompt injection, and multiple...
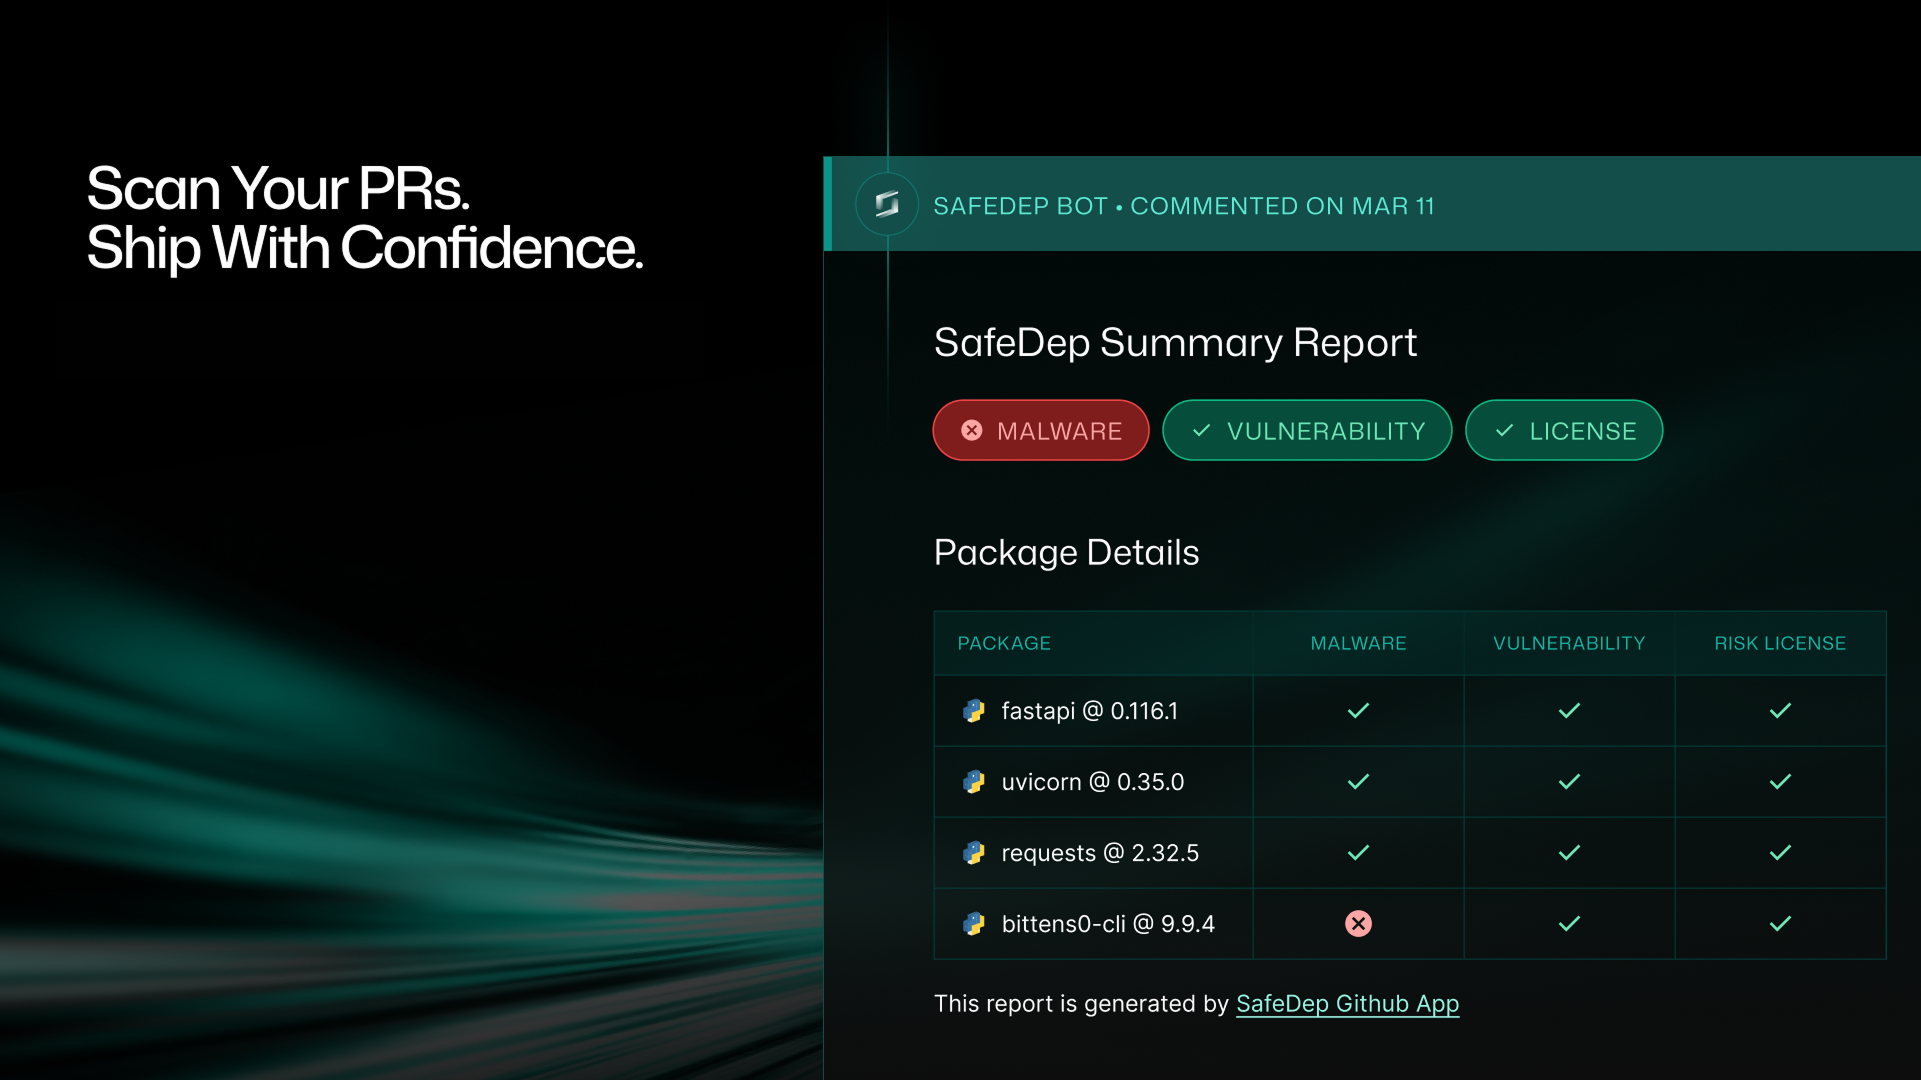
SafeDep launches a GitHub App for zero-configuration protection against malicious open source packages. Instantly scan pull requests and keep your code repositories safe from supply chain attacks.
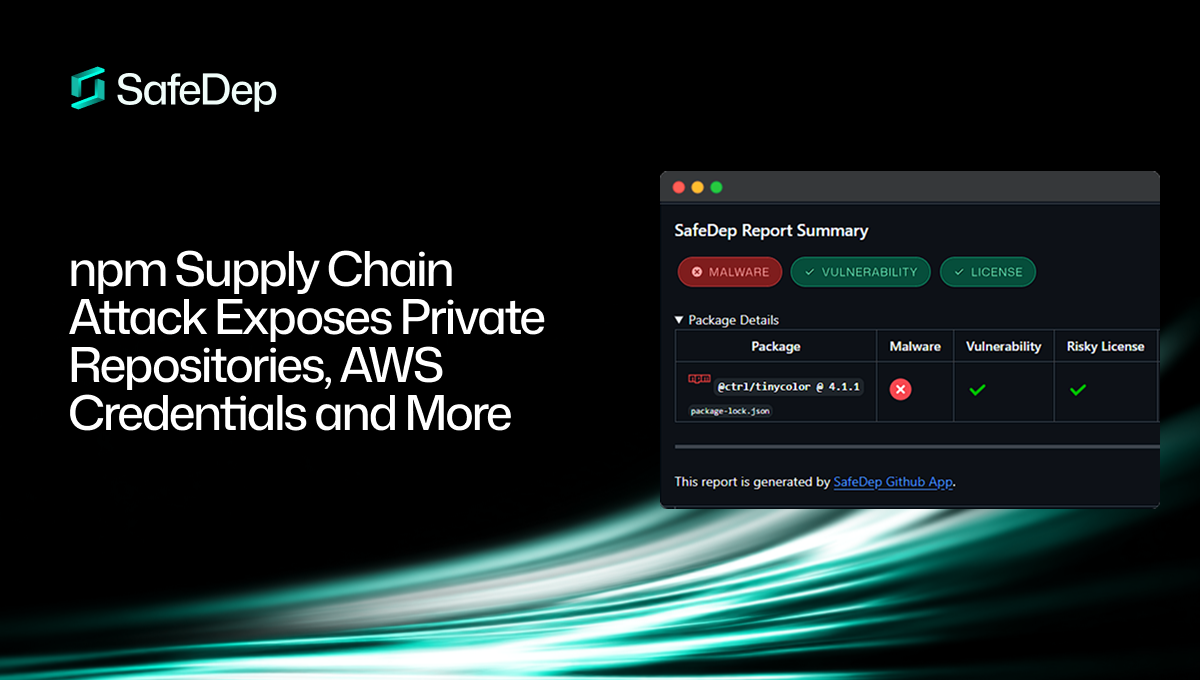
npm supply chain attacks continue. This time targeting @ctrl/tinycolor and multiple other packages with credential stealer malware. In this blog, we will analyze the attack and its impact on the npm...
Critical npm supply chain attack compromises zapier-sdk, @asyncapi, posthog, and @postman packages with self-replicating malware. Technical analysis reveals credential harvesting, GitHub Actions...
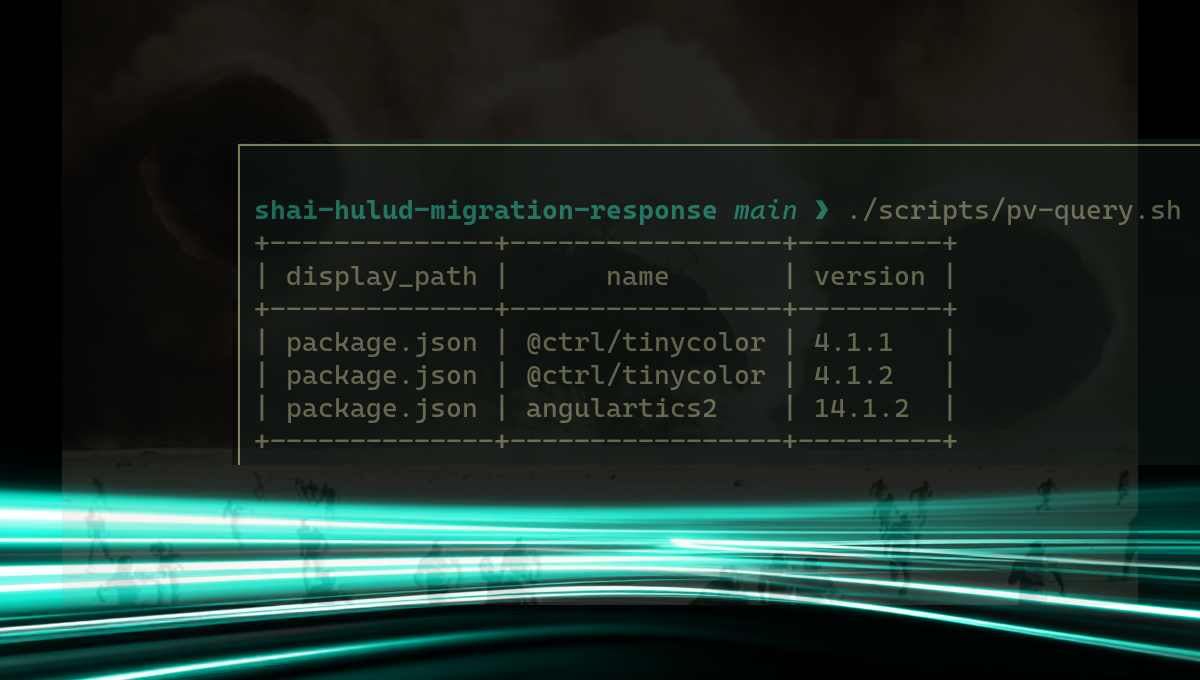
The Shai-Hulud supply chain attack is a major incident targeting developers through malicious packages in the npm ecosystem. This post outlines the incident response steps that can be taken to...
SafeDep keeps analytics anonymous and cookie-free until you opt in. Accepting helps us understand product usage and improve your experience. Privacy Policy
Choose what you share. You can change this anytime from the footer.
