



Agentic Workflows for Malicious Package Analysis
Experiments with agentic workflows for malicious package analysis built using Claude Desktop, Model Context Protocol (MCP) server, static code analysis and SafeDep Cloud API tools.
Experiments with agentic workflows for malicious package analysis built using Claude Desktop, Model Context Protocol (MCP) server, static code analysis and SafeDep Cloud API tools.
Multiple npm packages impersonating popular package names were published to the npm registry including by a Snyk researcher apparently targeting internal packages at Cursor AI.
Malware hidden in open source library packages are real. In this article, we analyse the malicious npm package llm-oracle.
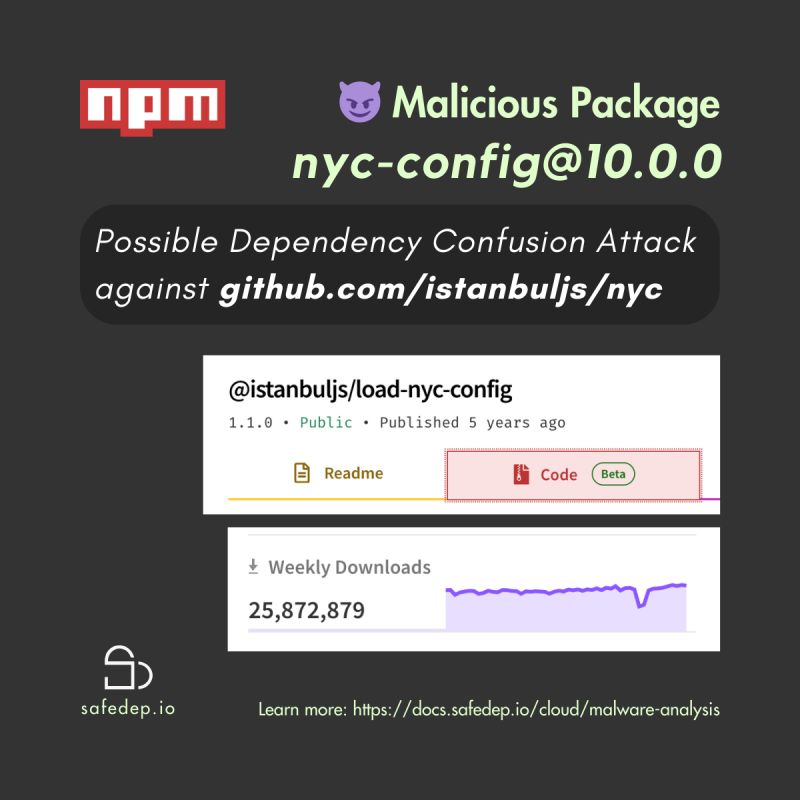
Possible typosquatting against @istanbuljs/load-nyc-config with ~25M weekly downloads.

Multiple npm packages impersonating popular package names are being used to distribute malware. We take a closer look at the campaign.
SafeDep keeps analytics anonymous and cookie-free until you opt in. Accepting helps us understand product usage and improve your experience. Privacy Policy
Choose what you share. You can change this anytime from the footer.
